

200-201 Exam Question 81
An analyst is investigating a host in the network that appears to be communicating to a command and control server on the Internet. After collecting this packet capture, the analyst cannot determine the technique and payload used for the communication.
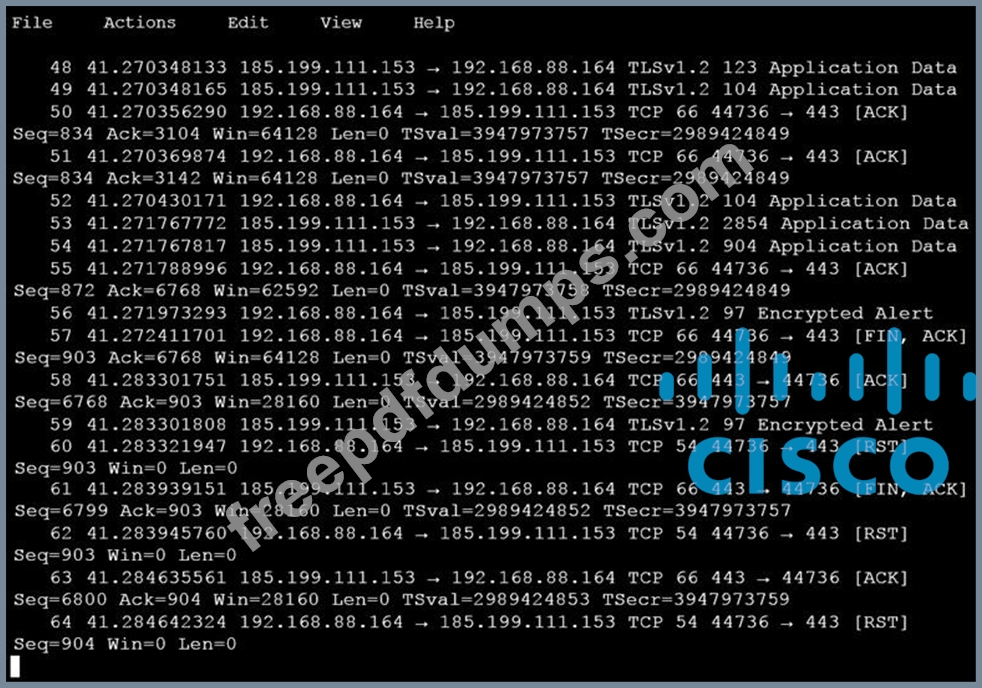
Which obfuscation technique is the attacker using?
Which obfuscation technique is the attacker using?
200-201 Exam Question 82

Refer to the exhibit. Which application protocol is in this PCAP file?
200-201 Exam Question 83
Refer to the exhibit.
In which Linux log file is this output found?
In which Linux log file is this output found?
200-201 Exam Question 84
Which two elements of the incident response process are stated in NIST Special Publication 800-61 r2? (Choose two.)
200-201 Exam Question 85
An engineer receives a security alert that traffic with a known TOR exit node has occurred on the network. What is the impact of this traffic?