

200-201 Exam Question 136
What is the principle of defense-in-depth?
200-201 Exam Question 137
Refer to the exhibit.

Which application-level protocol is being targeted?
Which application-level protocol is being targeted?
200-201 Exam Question 138
Which system monitors local system operation and local network access for violations of a security policy?
200-201 Exam Question 139
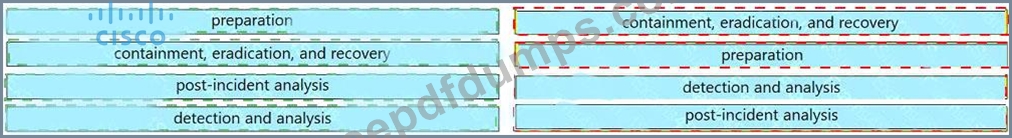
Drag and drop the elements from the left into the correct order for incident handling on the right.


200-201 Exam Question 140
The SOC team has confirmed a potential indicator of compromise on an endpoint. The team has narrowed the executable file's type to a new trojan family. According to the NIST Computer Security Incident Handling Guide, what is the next step in handling this event?