

CAS-004 Exam Question 296
A security analyst is concerned that a malicious piece of code was downloaded on a Linux system. After some research, the analyst determines that the suspected piece of code is performing a lot of input/output (I/O) on the disk drive.
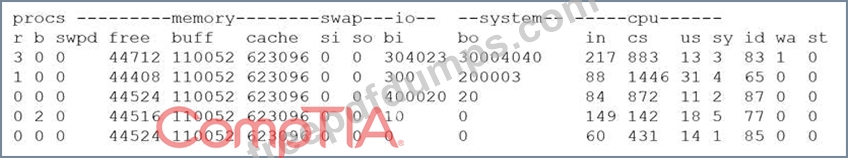
Based on the output above, from which of the following process IDs can the analyst begin an investigation?
Based on the output above, from which of the following process IDs can the analyst begin an investigation?
CAS-004 Exam Question 297
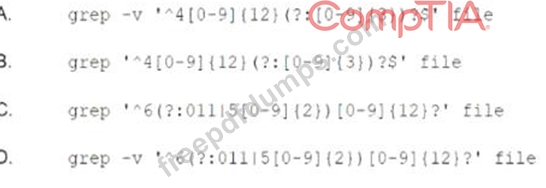
An organization's finance system was recently attacked. A forensic analyst is reviewing the contents of the compromised files for credit card data. Which of the following commands should the analyst run to BEST determine whether financial data was lost?
CAS-004 Exam Question 298
A company's Chief Information Security Officer is concerned that the company's proposed move to the cloud could lead to a lack of visibility into network traffic flow logs within the VPC.
Which of the following compensating controls would be BEST to implement in this situation?
Which of the following compensating controls would be BEST to implement in this situation?
CAS-004 Exam Question 299
Given the following log snippet from a web server:
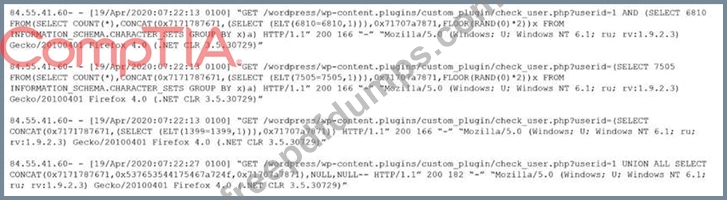
Which of the following BEST describes this type of attack?
Which of the following BEST describes this type of attack?
CAS-004 Exam Question 300
A company is deploying multiple VPNs to support supplier connections into its extranet applications. The network security standard requires:
* All remote devices to have up-to-date antivirus
* An up-to-date and patched OS
Which of the following technologies should the company deploy to meet its security objectives? (Select TWO)
* All remote devices to have up-to-date antivirus
* An up-to-date and patched OS
Which of the following technologies should the company deploy to meet its security objectives? (Select TWO)