

CAS-004 Exam Question 131
A security analyst is participating in a risk assessment and is helping to calculate the exposure factor associated with various systems and processes within the organization. Which of the following resources would be most useful to calculate the exposure factor in this scenario?
CAS-004 Exam Question 132
An e-commerce company is running a web server on premises, and the resource utilization is usually less than
30%. During the last two holiday seasons, the server experienced performance issues because of too many connections, and several customers were not able to finalize purchase orders. The company is looking to change the server configuration to avoid this kind of performance issue.
Which of the following is the MOST cost-effective solution?
CAS-004 Exam Question 133
Which of the following BEST describe the importance of maintaining chain of custody in forensic evidence collection? (Choose two.)
CAS-004 Exam Question 134
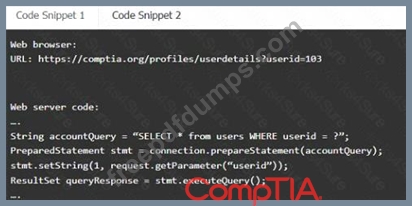
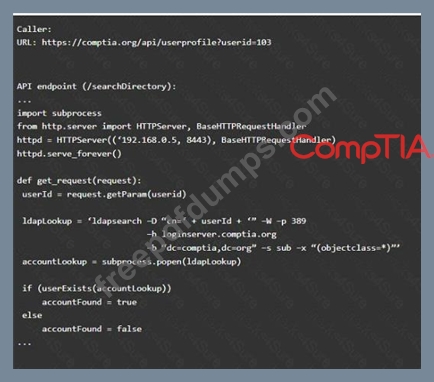
A product development team has submitted code snippets for review prior to release.
INSTRUCTIONS
Analyze the code snippets, and then select one vulnerability, and one fix for each code snippet.
Code Snippet 1
Code Snippet 2
Vulnerability 1:
* SQL injection
* Cross-site request forgery
* Server-side request forgery
* Indirect object reference
* Cross-site scripting
Fix 1:
* Perform input sanitization of the userid field.
* Perform output encoding of queryResponse,
* Ensure usex:ia belongs to logged-in user.
* Inspect URLS and disallow arbitrary requests.
* Implement anti-forgery tokens.
Vulnerability 2
1) Denial of service
2) Command injection
3) SQL injection
4) Authorization bypass
5) Credentials passed via GET
Fix 2
A) Implement prepared statements and bind
variables.
B) Remove the serve_forever instruction.
C) Prevent the "authenticated" value from being overridden by a GET parameter.
D) HTTP POST should be used for sensitive parameters.
E) Perform input sanitization of the userid field.
INSTRUCTIONS
Analyze the code snippets, and then select one vulnerability, and one fix for each code snippet.
Code Snippet 1
Code Snippet 2
Vulnerability 1:
* SQL injection
* Cross-site request forgery
* Server-side request forgery
* Indirect object reference
* Cross-site scripting
Fix 1:
* Perform input sanitization of the userid field.
* Perform output encoding of queryResponse,
* Ensure usex:ia belongs to logged-in user.
* Inspect URLS and disallow arbitrary requests.
* Implement anti-forgery tokens.
Vulnerability 2
1) Denial of service
2) Command injection
3) SQL injection
4) Authorization bypass
5) Credentials passed via GET
Fix 2
A) Implement prepared statements and bind
variables.
B) Remove the serve_forever instruction.
C) Prevent the "authenticated" value from being overridden by a GET parameter.
D) HTTP POST should be used for sensitive parameters.
E) Perform input sanitization of the userid field.
CAS-004 Exam Question 135
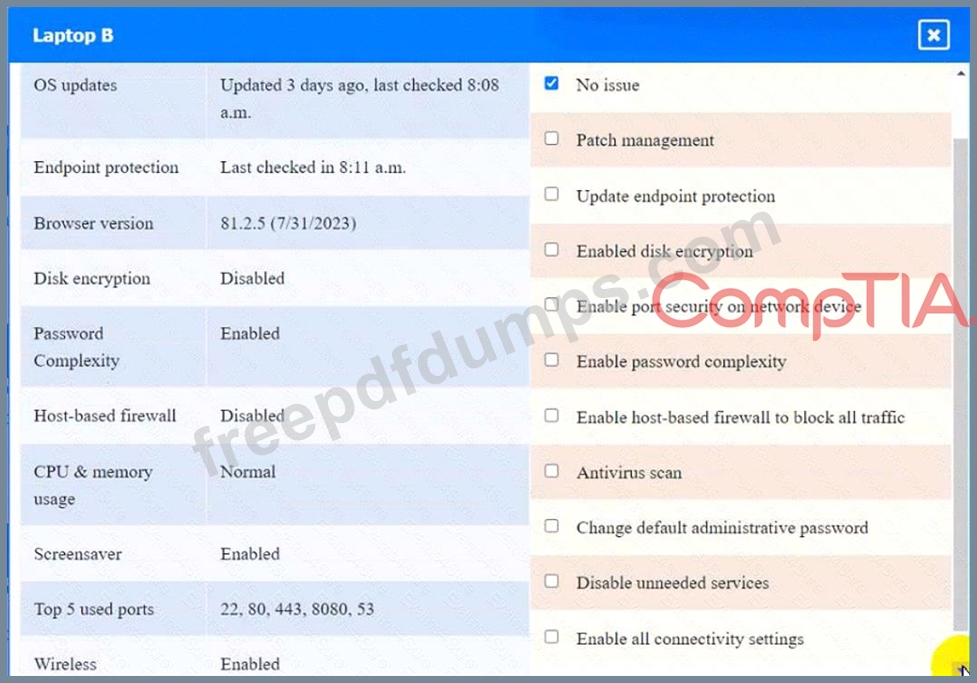
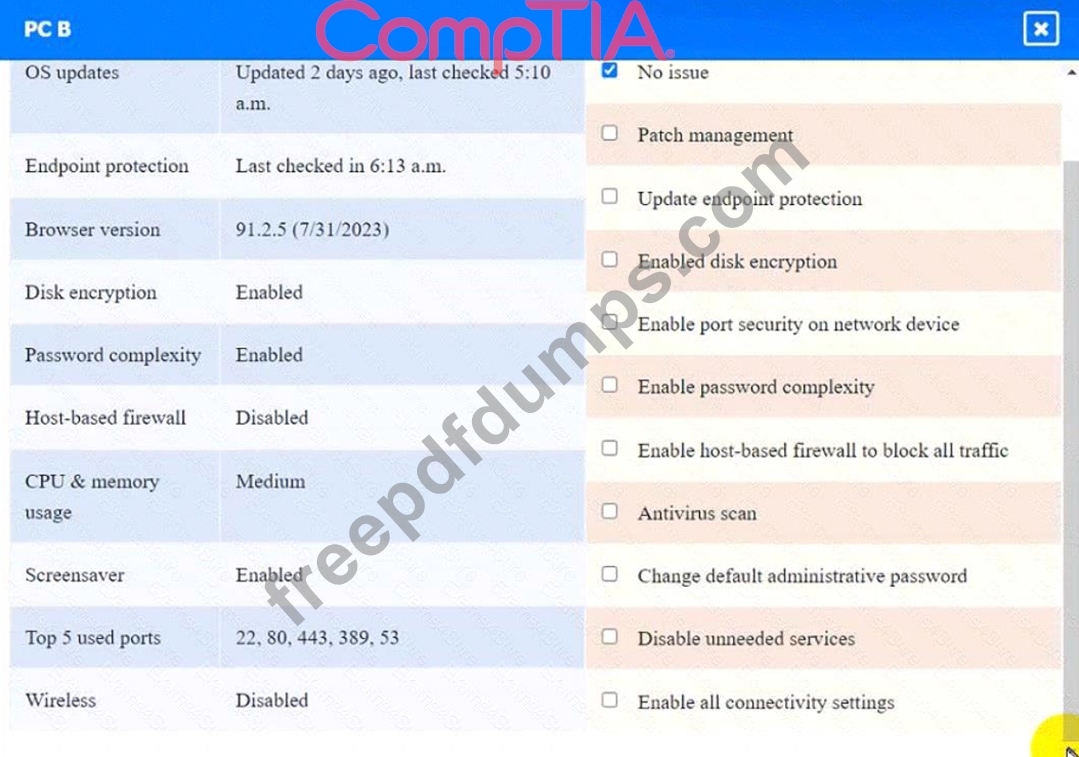
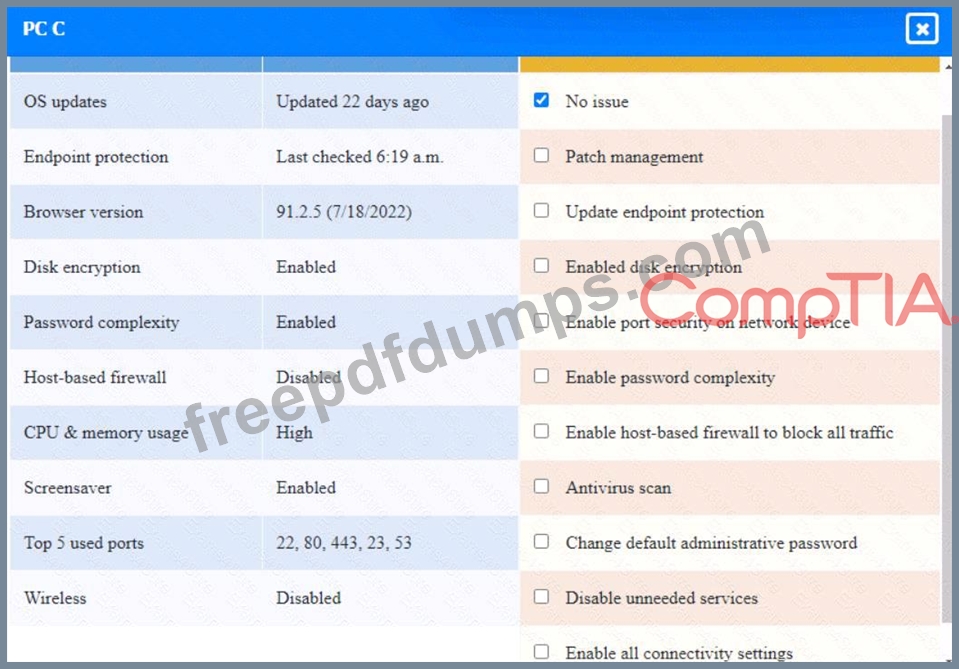
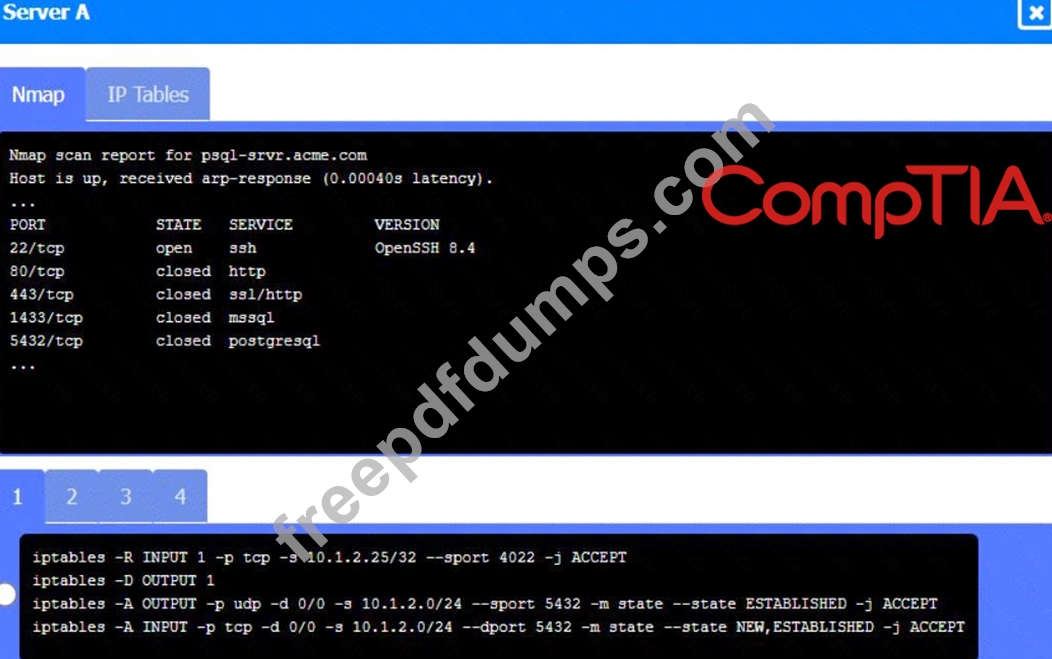
A security engineer needs to review the configurations of several devices on the network to meet the following requirements:
* The PostgreSQL server must only allow connectivity in the 10.1.2.0/24 subnet.
* The SSH daemon on the database server must be configured to listen
to port 4022.
* The SSH daemon must only accept connections from a Single
workstation.
* All host-based firewalls must be disabled on all workstations.
* All devices must have the latest updates from within the past eight
days.
* All HDDs must be configured to secure data at rest.
* Cleartext services are not allowed.
* All devices must be hardened when possible.
Instructions:
Click on the various workstations and network devices to review the posture assessment results. Remediate any possible issues or indicate that no issue is found.
Click on Server A to review output data. Select commands in the appropriate tab to remediate connectivity problems to the pOSTGREsql DATABASE VIA ssh
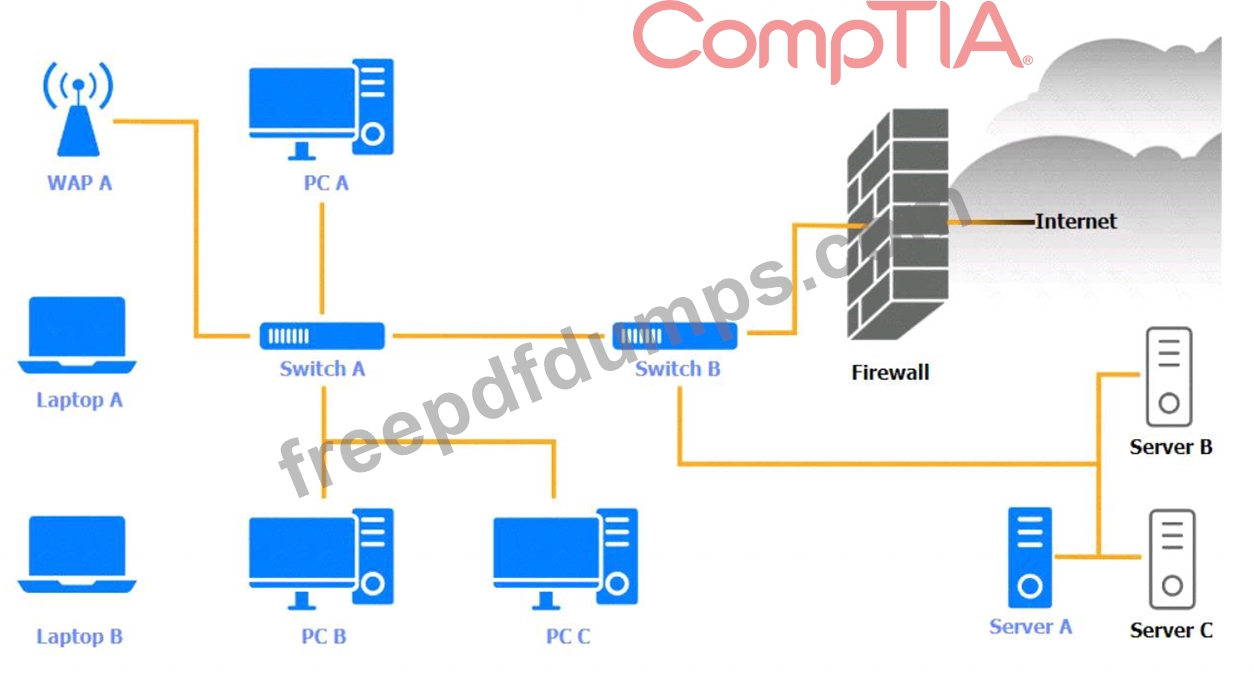
WAP A
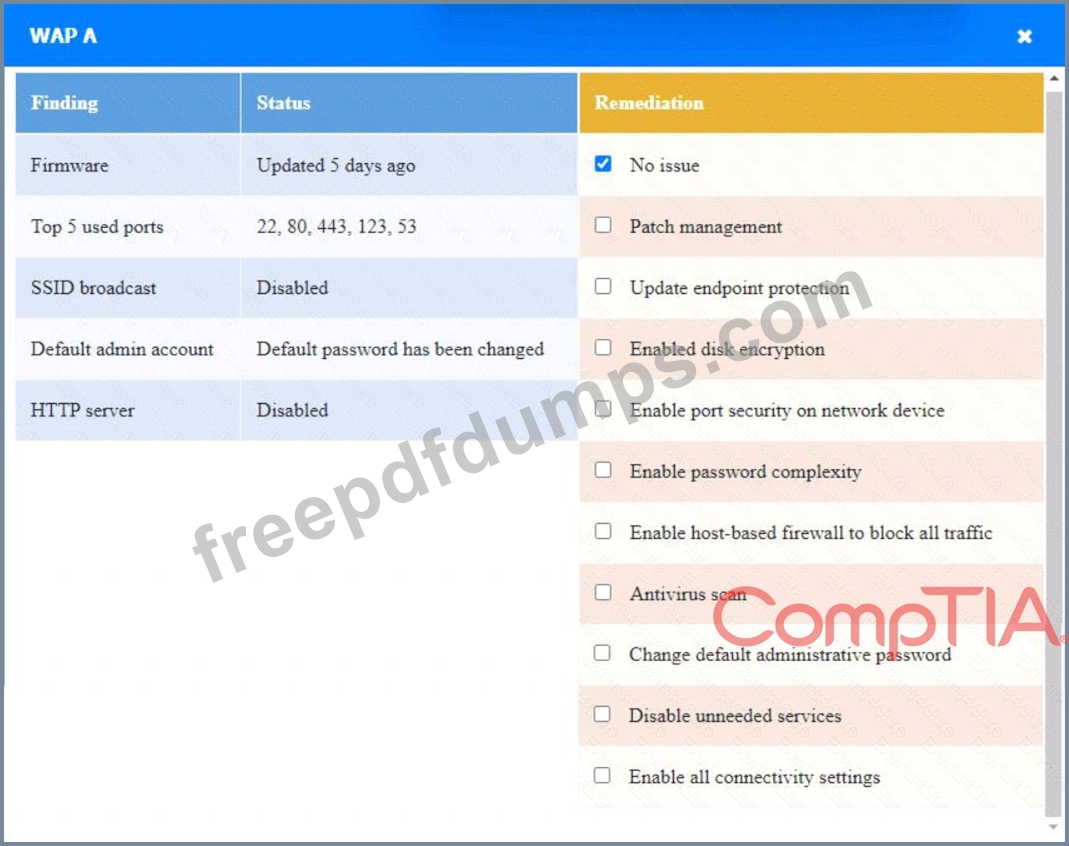
PC A
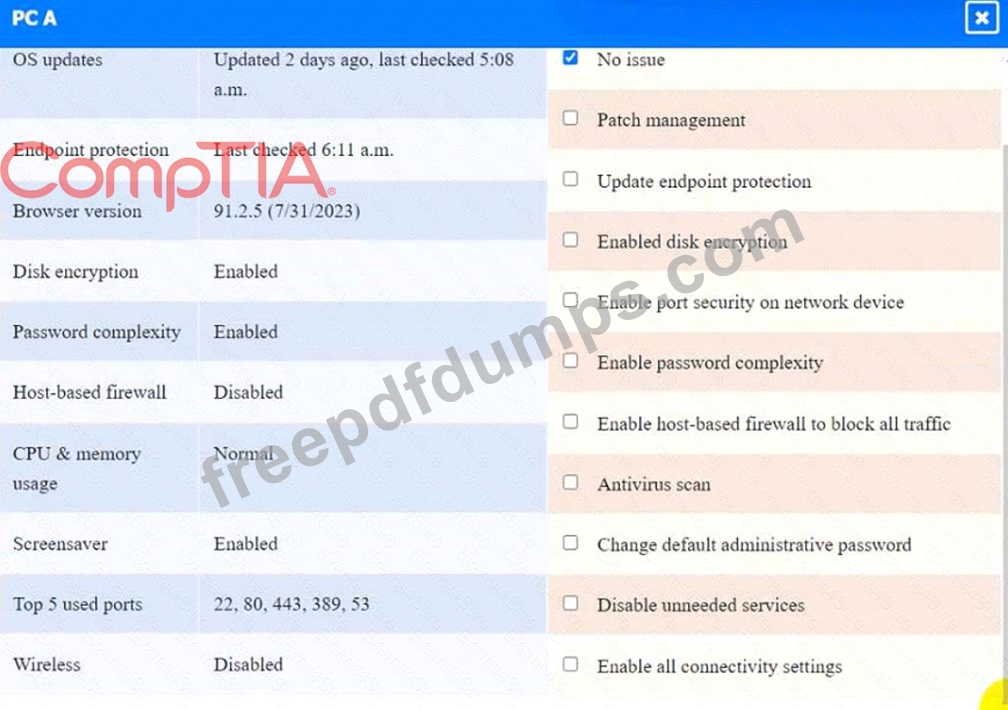
Laptop A
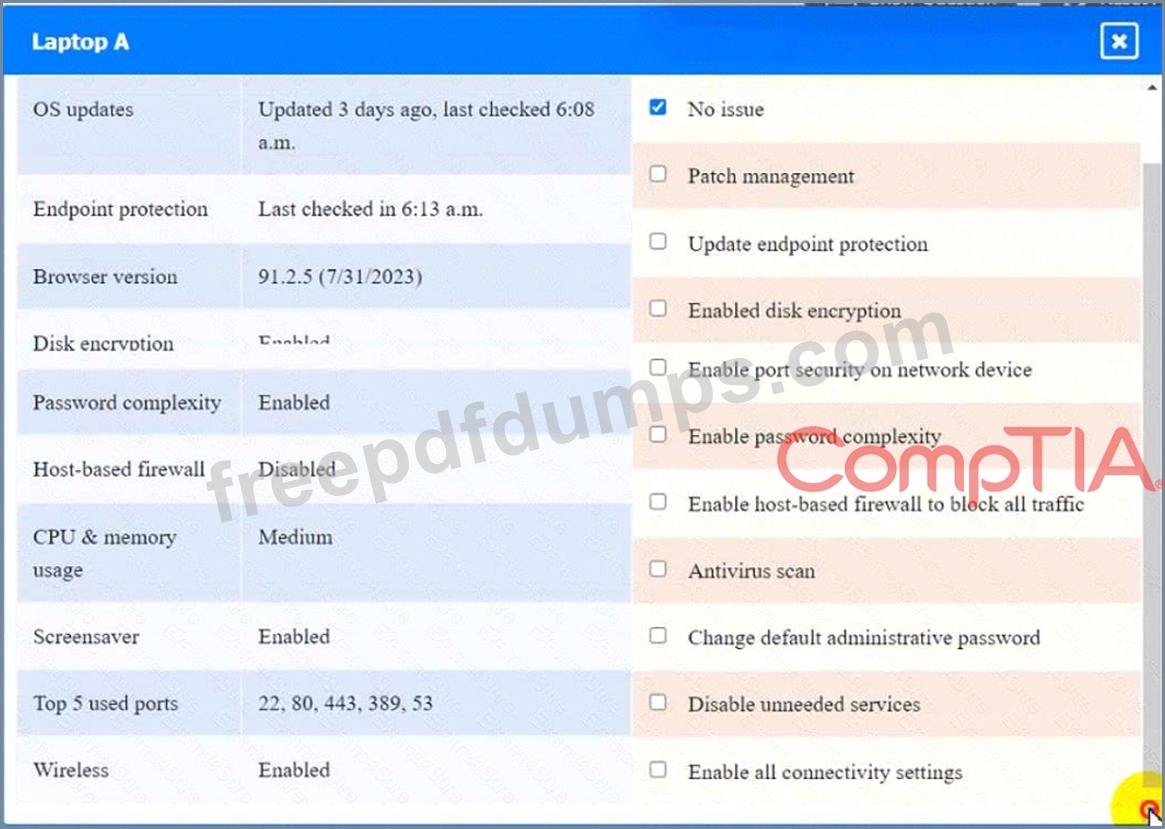
Switch A
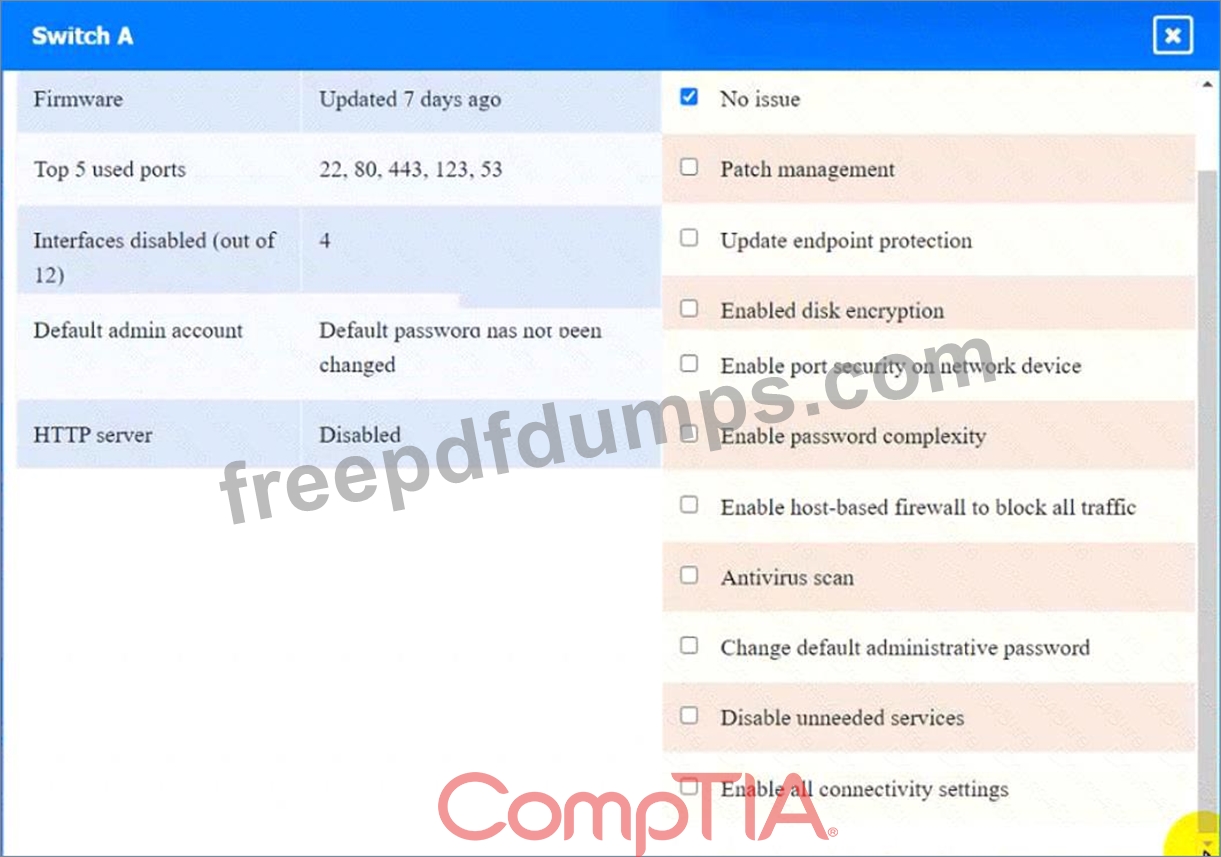
Switch B:
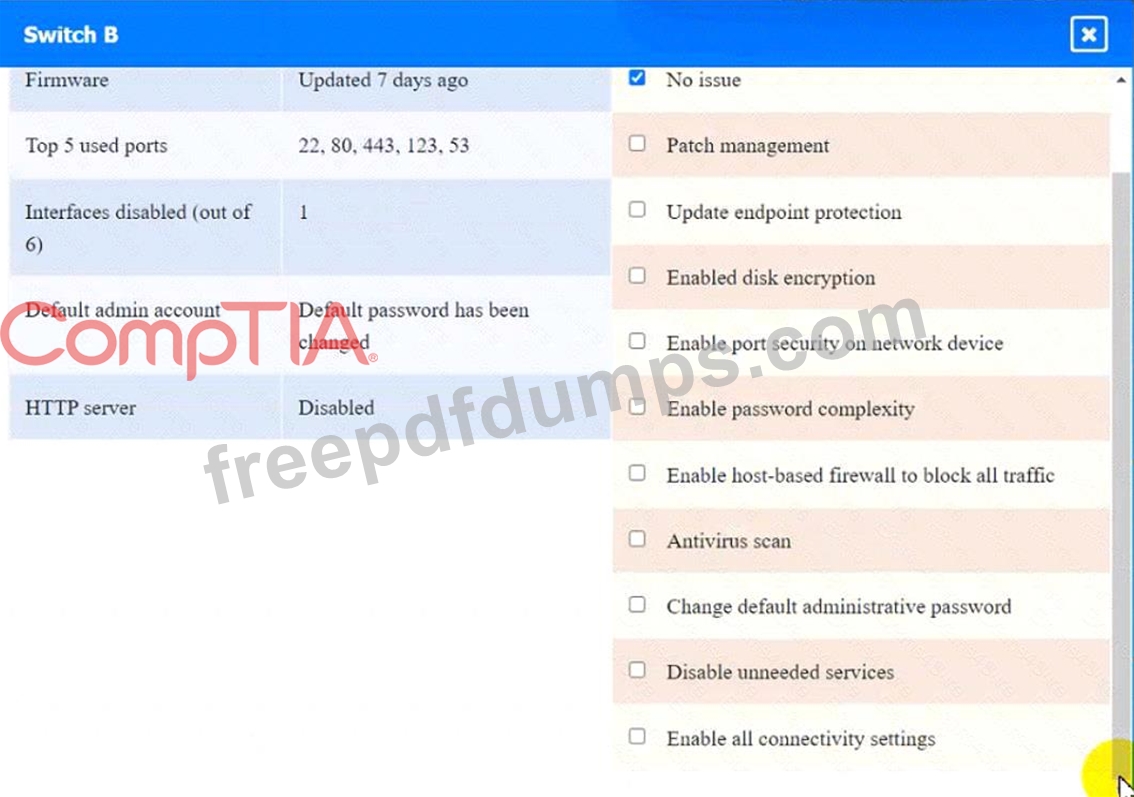
Laptop B
PC B
PC C
Server A
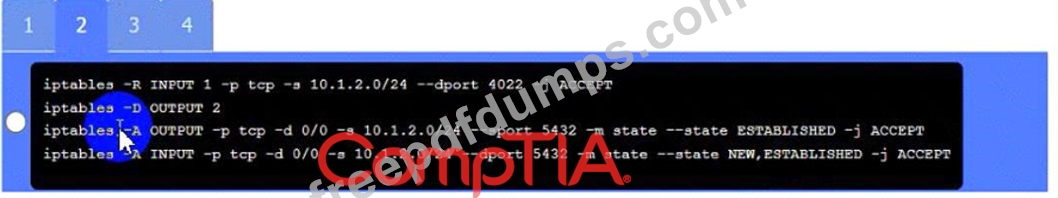
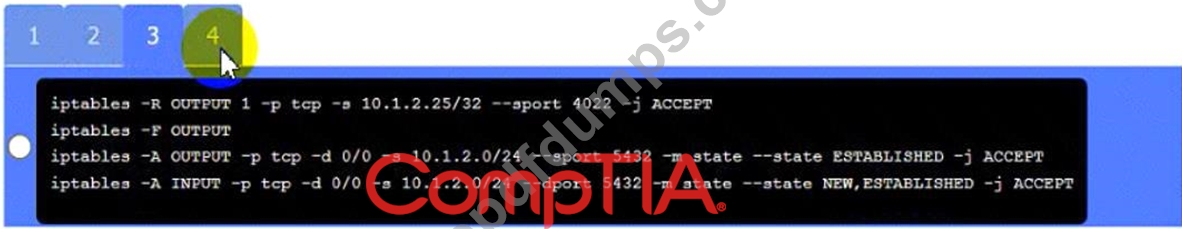
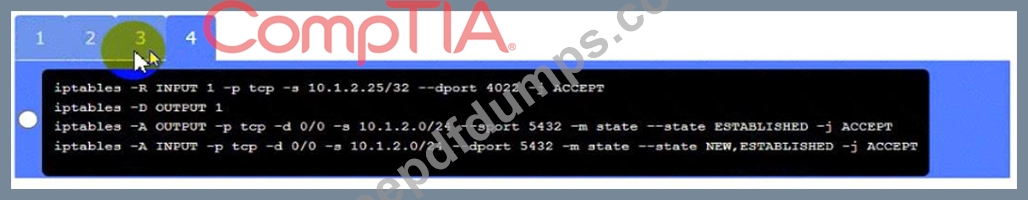
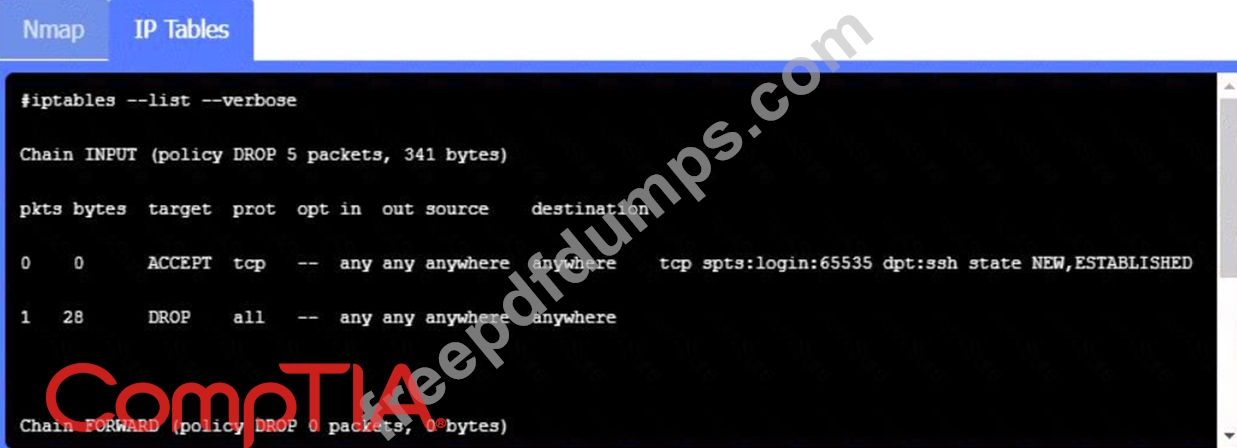
* The PostgreSQL server must only allow connectivity in the 10.1.2.0/24 subnet.
* The SSH daemon on the database server must be configured to listen
to port 4022.
* The SSH daemon must only accept connections from a Single
workstation.
* All host-based firewalls must be disabled on all workstations.
* All devices must have the latest updates from within the past eight
days.
* All HDDs must be configured to secure data at rest.
* Cleartext services are not allowed.
* All devices must be hardened when possible.
Instructions:
Click on the various workstations and network devices to review the posture assessment results. Remediate any possible issues or indicate that no issue is found.
Click on Server A to review output data. Select commands in the appropriate tab to remediate connectivity problems to the pOSTGREsql DATABASE VIA ssh
WAP A
PC A
Laptop A
Switch A
Switch B:
Laptop B
PC B
PC C
Server A