

CAS-004 Exam Question 306
A large number of emails have been reported, and a security analyst is reviewing the following information from the emails:
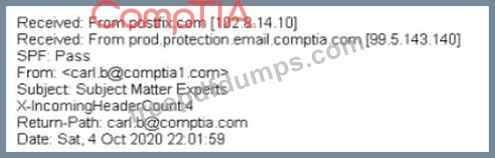
As part of the image process, which of the following is the FIRST step the analyst should take?
As part of the image process, which of the following is the FIRST step the analyst should take?
CAS-004 Exam Question 307
A security analyst notices a number of SIEM events that show the following activity:

Which of the following response actions should the analyst take FIRST?
Which of the following response actions should the analyst take FIRST?
CAS-004 Exam Question 308
A small business requires a low-cost approach to theft detection for the audio recordings it produces and sells.
Which of the following techniques will MOST likely meet the business's needs?
Which of the following techniques will MOST likely meet the business's needs?
CAS-004 Exam Question 309
A security architect is given the following requirements to secure a rapidly changing enterprise with an increasingly distributed and remote workforce:
- Cloud-delivered services
- Full network security stack
- SaaS application security management
- Minimal latency for an optimal user experience
- Integration with the cloud 1AM platform
Which of the following is the BEST solution?
- Cloud-delivered services
- Full network security stack
- SaaS application security management
- Minimal latency for an optimal user experience
- Integration with the cloud 1AM platform
Which of the following is the BEST solution?
CAS-004 Exam Question 310
Ann, a CIRT member, is conducting incident response activities on a network that consists of several hundred virtual servers and thousands of endpoints and users. The network generates more than 10,000 log messages per second. The enterprise belong to a large, web-based cryptocurrency startup, Ann has distilled the relevant information into an easily digestible report for executive management . However, she still needs to collect evidence of the intrusion that caused the incident. Which of the following should Ann use to gather the required information?