

CAS-004 Exam Question 351
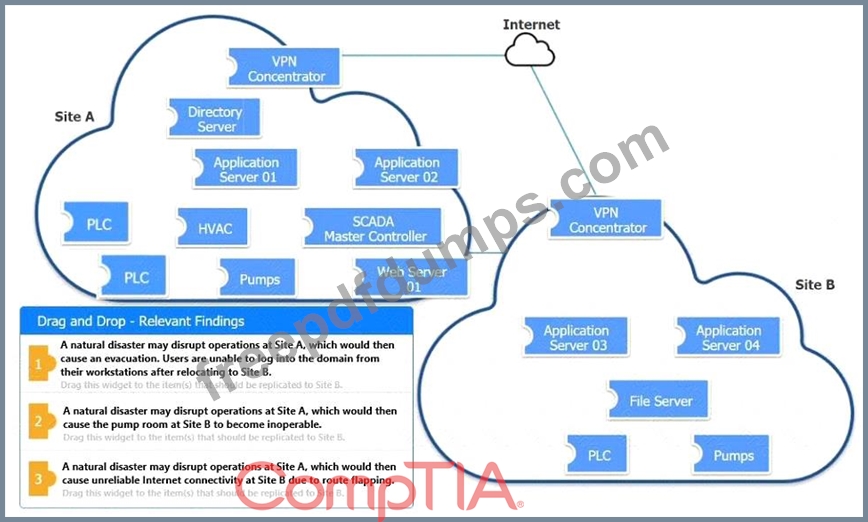
An organization is planning for disaster recovery and continuity of operations.
INSTRUCTIONS
Review the following scenarios and instructions. Match each relevant finding to the affected host.
After associating scenario 3 with the appropriate host(s), click the host to select the appropriate corrective action for that finding.
Each finding may be used more than once.
If at any time you would like to bring back the initial state of the simul-ation, please click the Reset All button.


CAS-004 Exam Question 352
Which of the following represents the MOST significant benefit of implementing a passwordless authentication solution?
CAS-004 Exam Question 353
A threat analyst notices the following URL while going through the HTTP logs.

Which of the following attack types is the threat analyst seeing?
Which of the following attack types is the threat analyst seeing?
CAS-004 Exam Question 354
Which of the following is the best reason for obtaining file hashes from a confiscated laptop?
CAS-004 Exam Question 355
An organization developed a containerized application. The organization wants to run the application in the cloud and automatically scale it based on demand. The security operations team would like to use container orchestration but does not want to assume patching responsibilities. Which of the following service models best meets these requirements?