

CAS-005 Exam Question 111
SIMULATION
You are a security analyst tasked with interpreting an Nmap scan output from company's privileged network.
The company's hardening guidelines indicate the following:
- There should be one primary server or service per device.
- Only default ports should be used.
- Non-secure protocols should be disabled.
INSTRUCTIONS
Using the Nmap output, identify the devices on the network and their roles, and any open ports that should be closed.
For each device found by Nmap, add a device entry to the Devices Discovered list, with the following information:
- The IP address of the device
- The primary server or service of the device (Note that each IP should by associated with one service/port only)
- The protocol(s) that should be disabled based on the hardening guidelines (Note that multiple ports may need to be closed to comply with the hardening guidelines) If at any time you would like to bring back the initial state of the simulation, please click the Reset All button.
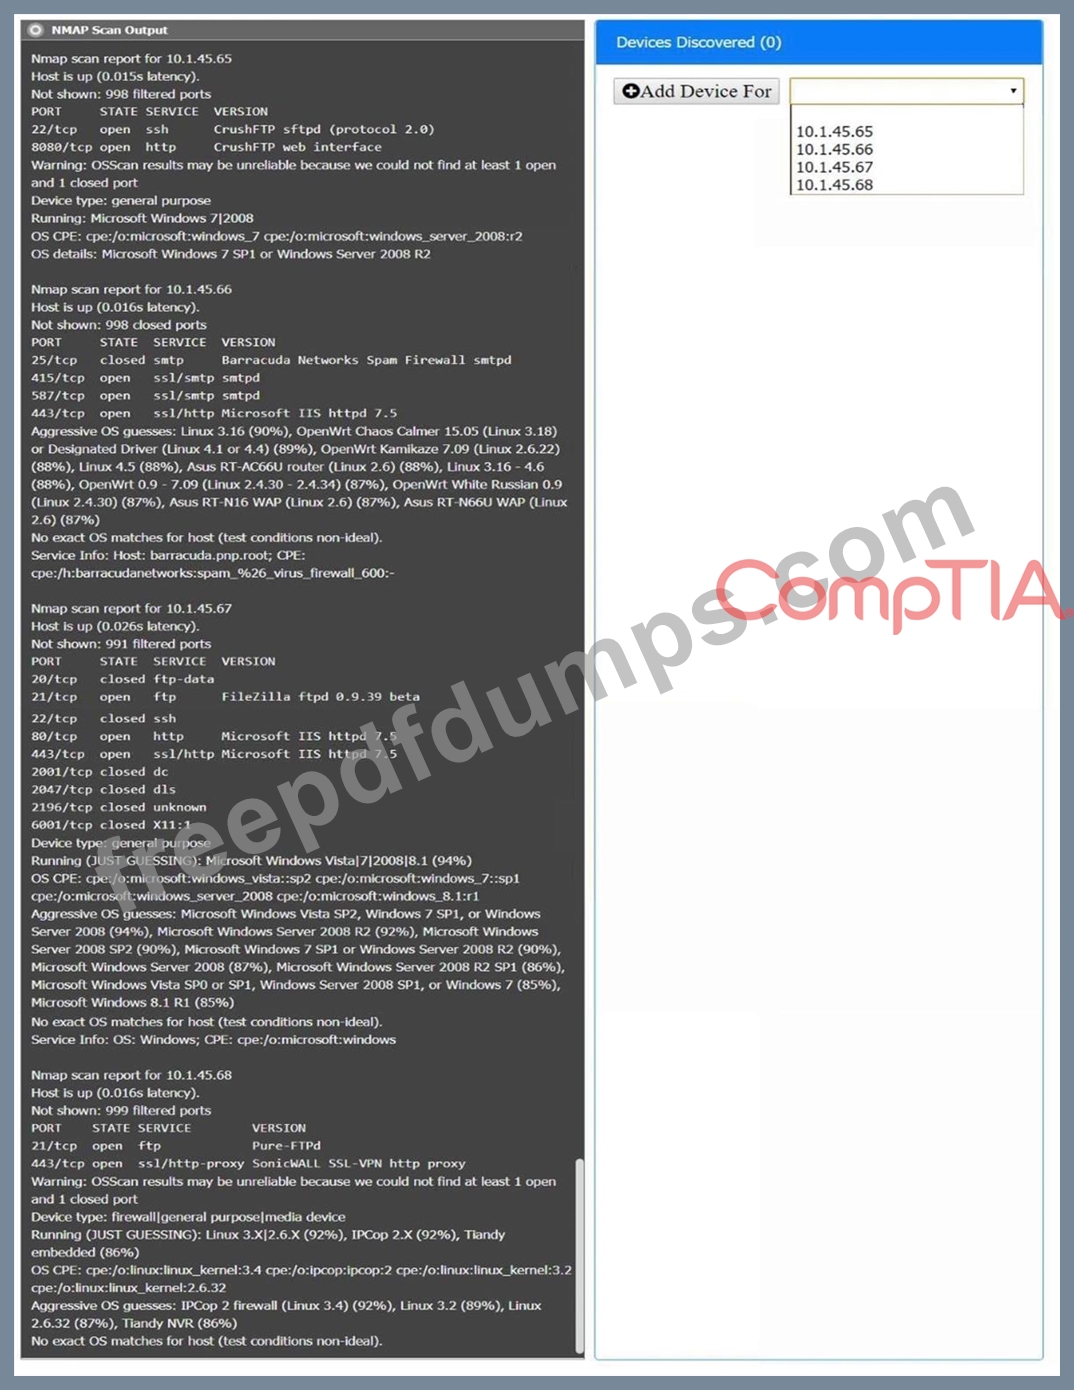
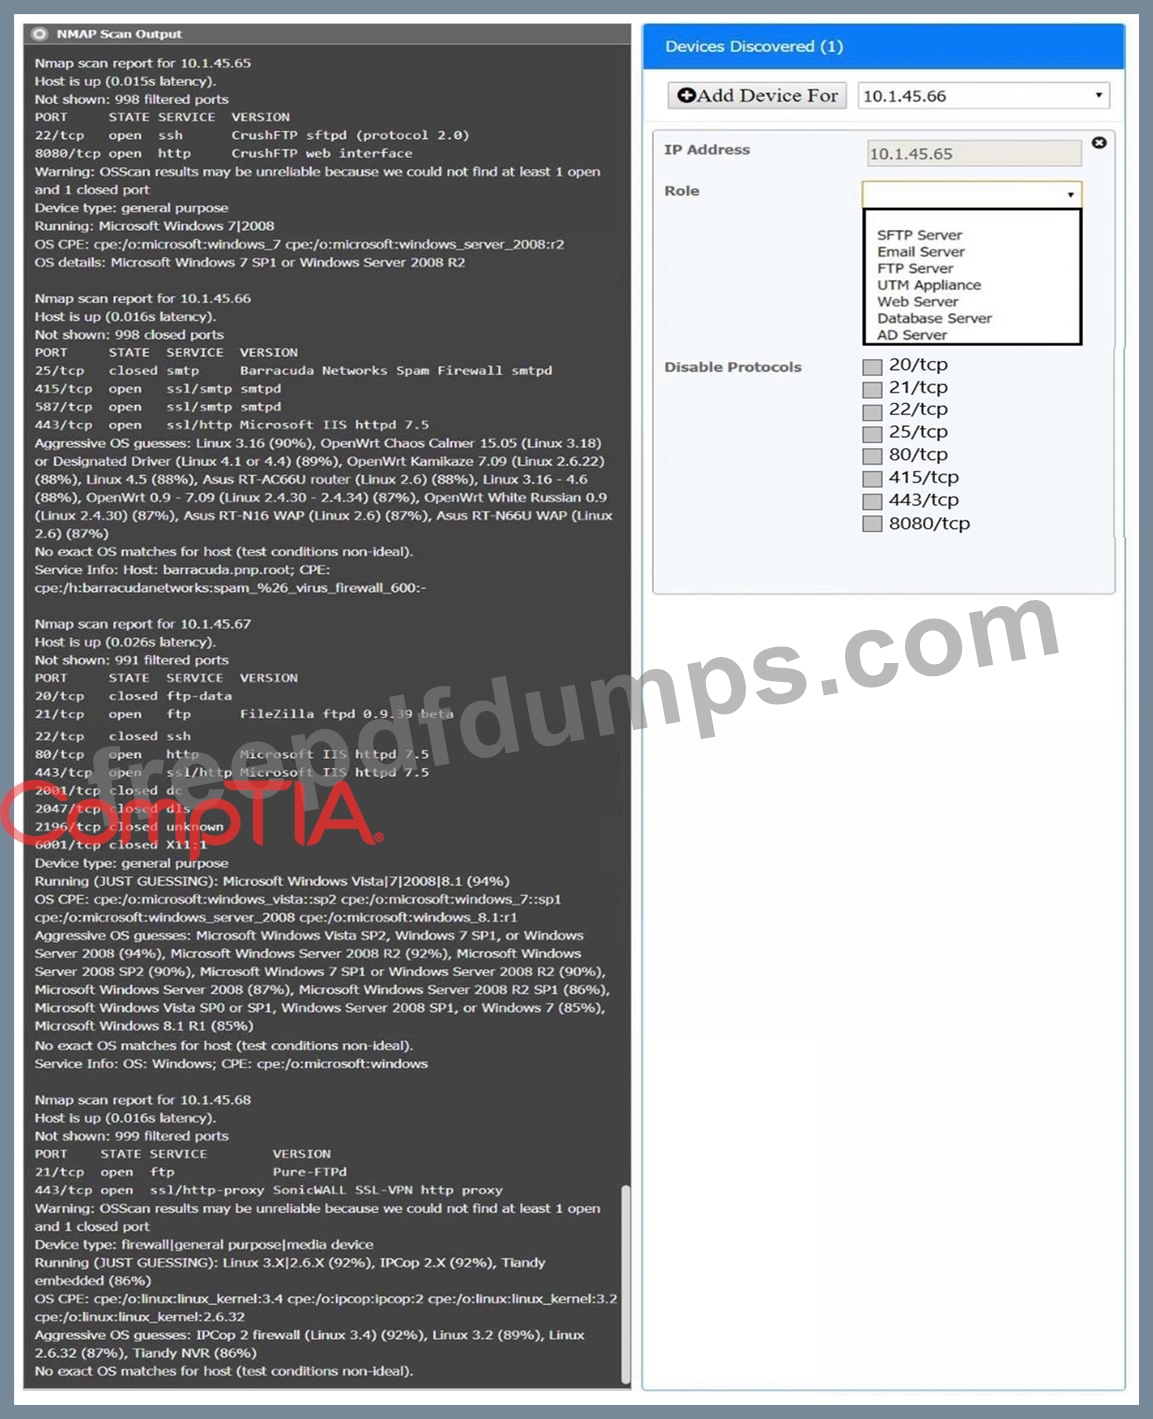
You are a security analyst tasked with interpreting an Nmap scan output from company's privileged network.
The company's hardening guidelines indicate the following:
- There should be one primary server or service per device.
- Only default ports should be used.
- Non-secure protocols should be disabled.
INSTRUCTIONS
Using the Nmap output, identify the devices on the network and their roles, and any open ports that should be closed.
For each device found by Nmap, add a device entry to the Devices Discovered list, with the following information:
- The IP address of the device
- The primary server or service of the device (Note that each IP should by associated with one service/port only)
- The protocol(s) that should be disabled based on the hardening guidelines (Note that multiple ports may need to be closed to comply with the hardening guidelines) If at any time you would like to bring back the initial state of the simulation, please click the Reset All button.
CAS-005 Exam Question 112
A company that uses containers to run its applications is required to identify vulnerabilities on every container image in a private repository. The security team needs to be able to quickly evaluate whether to respond to a given vulnerability. Which of the following will allow the security team to achieve the objective with the least effort?
CAS-005 Exam Question 113
A security analyst is reviewing the following log:
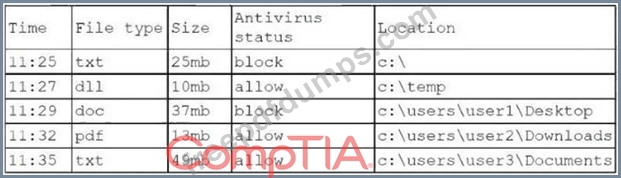
Which of the following possible events should the security analyst investigate further?
Which of the following possible events should the security analyst investigate further?
CAS-005 Exam Question 114
A compliance officer is reviewing the data sovereignty laws in several countries where the organization has no presence Which of the following is the most likely reason for reviewing these laws?
CAS-005 Exam Question 115
While reviewing recent modem reports, a security officer discovers that several employees were contacted by the same individual who impersonated a recruiter. Which of the following best describes this type of correlation?
Premium Bundle
Newest CAS-005 Exam PDF Dumps shared by Actual4test.com for Helping Passing CAS-005 Exam! Actual4test.com now offer the updated CAS-005 exam dumps, the Actual4test.com CAS-005 exam questions have been updated and answers have been corrected get the latest Actual4test.com CAS-005 pdf dumps with Exam Engine here:
(604 Q&As Dumps, 30%OFF Special Discount: Freepdfdumps)