

SY0-601 Exam Question 11
During a recent incident an external attacker was able to exploit an SMB vulnerability over the internet. Which of the following action items should a security analyst perform FIRST to prevent this from occurring again?
SY0-601 Exam Question 12
A user forwarded a suspicious email to the security team, Upon investigation, a malicious URL was discovered. Which of the following should be done FIRST to prevent other users from accessing the malicious URL?
SY0-601 Exam Question 13
After multiple on premises security solutions were migrated to the cloud, the incident response time increased.
The analyst are spending a long time to trace information on different cloud consoles and correlating data in different formats. Which of the following can be used to optimize the incident response time?
The analyst are spending a long time to trace information on different cloud consoles and correlating data in different formats. Which of the following can be used to optimize the incident response time?
SY0-601 Exam Question 14
A junior security analyst iss conducting an analysis after passwords were changed on multiple accounts without users' interaction. The SIEM have multiple logtn entnes with the following text:
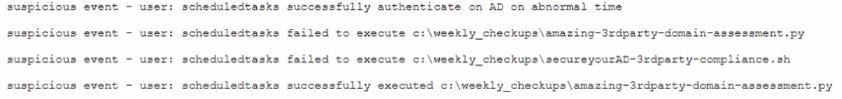
Which of Ihe following is the MOST likely attack conducted on the environment?
Which of Ihe following is the MOST likely attack conducted on the environment?
SY0-601 Exam Question 15
A company recently experienced a significant data loss when proprietary Information was leaked to a competitor. The company took special precautions by using proper labels; however, email filter logs do not have any record of the incident. An Investigation confirmed the corporate network was not breached, but documents were downloaded from an employee's COPE tablet and passed to the competitor via cloud storage.
Which of the following is the BEST remediation for this data leak?
Which of the following is the BEST remediation for this data leak?