

SY0-601 Exam Question 161
The process of passively gathering information prior to launching a cyberattack is called:
SY0-601 Exam Question 162
A company was compromised, and a security analyst discovered the attacker was able to get access to a service account. The following logs were discovered during the investigation:
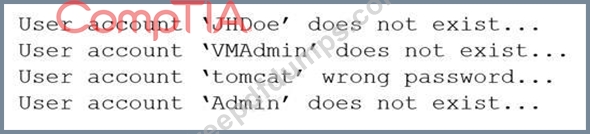
Which of the following MOST likely would have prevented the attacker from learning the service account name?
Which of the following MOST likely would have prevented the attacker from learning the service account name?
SY0-601 Exam Question 163
A security administrator checks the table of a network switch, which shows the following output:
Which of the following is happening to this switch?
Which of the following is happening to this switch?
SY0-601 Exam Question 164
A startup company is using multiple SaaS and IaaS platforms to stand up a corporate infrastructure and build out a customer-facing web application. Which of the following solutions would be BEST to provide security, manageability, and visibility into the platforms?
SY0-601 Exam Question 165
Certain users are reporting their accounts are being used to send unauthorized emails and conduct suspicious activities. After further investigation, a security analyst notices the following:
* All users share workstations throughout the day.
* Endpoint protection was disabled on several workstations throughout the network.
* Travel times on logins from the affected users are impossible.
* Sensitive data is being uploaded to external sites.
* All user account passwords were forced to be reset and the issue continued.
Which of the following attacks is being used to compromise the user accounts?