

CS0-002 Exam Question 66
A security analyst discovered a specific series of IP addresses that are targeting an organization.
None of the attacks have been successful. Which of the following should the security analyst perform NEXT?
None of the attacks have been successful. Which of the following should the security analyst perform NEXT?
CS0-002 Exam Question 67
A development team uses open-source software and follows an Agile methodology with two-week sprints. Last month, the security team filed a bug for an insecure version of a common library. The DevOps team updated the library on the server, and then the security team rescanned the server to verify it was no longer vulnerable.
This month, the security team found the same vulnerability on the server.
Which of the following should be done to correct the cause of the vulnerability?
This month, the security team found the same vulnerability on the server.
Which of the following should be done to correct the cause of the vulnerability?
CS0-002 Exam Question 68
An analyst is examining a system that is suspected of being involved in an intrusion.
The analyst uses the command `cat/etc/passwd' and receives the following partial output:

Based on the above output, which of the following should the analyst investigate further?
The analyst uses the command `cat/etc/passwd' and receives the following partial output:
Based on the above output, which of the following should the analyst investigate further?
CS0-002 Exam Question 69
An organization that handles sensitive financial information wants to perform tokenization of data to enable the execution of recurring transactions. The organization is most interested in a secure, built-in device to support its solution. Which of the following would MOST likely be required to perform the desired function?
CS0-002 Exam Question 70
A security analyst is reviewing the logs from an internal chat server. The chat.log file is too large to review manually, so the analyst wants to create a shorter log file that only includes lines associated with a user demonstrating anomalous activity. Below is a snippet of the log:
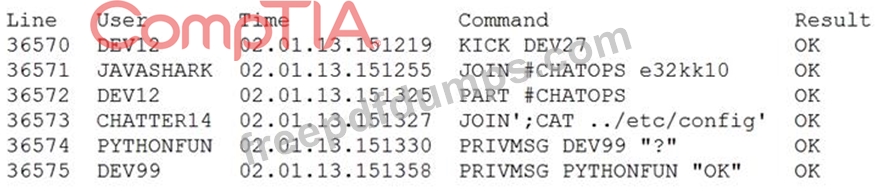
Which of the following commands would work BEST to achieve the desired result?
Which of the following commands would work BEST to achieve the desired result?