

MS-102 Exam Question 51
HOTSPOT
You have a Microsoft 365 subscription.
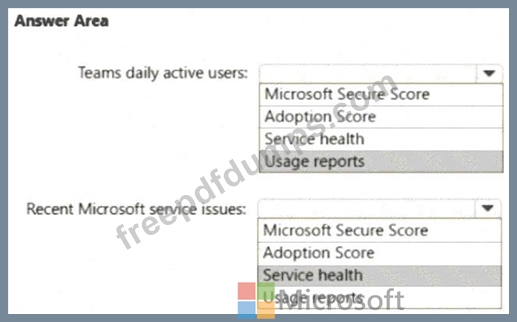
You need to review metrics for the following:
The daily active users in Microsoft Teams
Recent Microsoft service issues
What should you use? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.

You have a Microsoft 365 subscription.
You need to review metrics for the following:
The daily active users in Microsoft Teams
Recent Microsoft service issues
What should you use? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.

MS-102 Exam Question 52
Your company has three main offices and one branch office. The branch office is used for research.
The company plans to implement a Microsoft 365 tenant and to deploy multi-factor authentication.
You need to recommend a Microsoft 365 solution to ensure that multi-factor authentication is enforced only for users in the branch office.
What should you include in the recommendation?
The company plans to implement a Microsoft 365 tenant and to deploy multi-factor authentication.
You need to recommend a Microsoft 365 solution to ensure that multi-factor authentication is enforced only for users in the branch office.
What should you include in the recommendation?
MS-102 Exam Question 53
You have a Microsoft 365 E5 subscription that contains the resources shown in the following table.
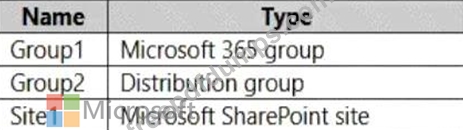
You create a sensitivity label named Label1.
To which resource can you apply Label1?
You create a sensitivity label named Label1.
To which resource can you apply Label1?
MS-102 Exam Question 54
You have a Microsoft 365 E5 subscription that contains the devices shown in the following table.
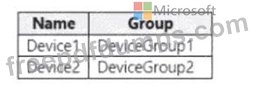
At 08:00. you create an incident notification rule that has the following configurations:
* Name: Notification!
* Notification settings
o Notify on alert seventy: Low
o Device group scope: All (3)
o Details: First notification per incident
* Recipients: [email protected], [email protected]
At 08:02. you create an incident notification rule that has the following configurations:
* Name: Notification
* Notification settings
o Notify on alert severity: Low. Medium
o Device group scope: DevtceGroup1, DeviceGroup2
* Recipients: [email protected]
in Microsoft Defender XDR, alerts are logged as shown in the following table.

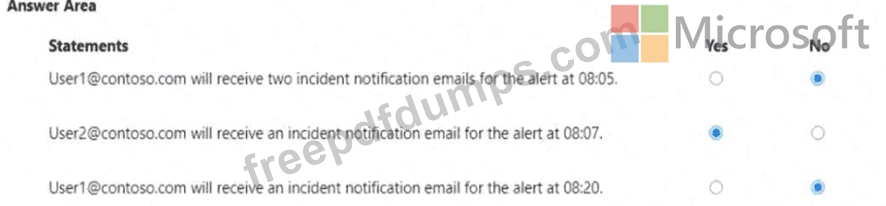
For each of the following statements, select Yes if the statement is true. Otherwise, select No1.
NOTE: Each correct selection is worth one point.

At 08:00. you create an incident notification rule that has the following configurations:
* Name: Notification!
* Notification settings
o Notify on alert seventy: Low
o Device group scope: All (3)
o Details: First notification per incident
* Recipients: [email protected], [email protected]
At 08:02. you create an incident notification rule that has the following configurations:
* Name: Notification
* Notification settings
o Notify on alert severity: Low. Medium
o Device group scope: DevtceGroup1, DeviceGroup2
* Recipients: [email protected]
in Microsoft Defender XDR, alerts are logged as shown in the following table.
For each of the following statements, select Yes if the statement is true. Otherwise, select No1.
NOTE: Each correct selection is worth one point.

MS-102 Exam Question 55
You have a hybrid deployment of Microsoft 365 that contains the users shown in the following table.

Microsoft Entra Connect Sync has the following settings:
Password Hash Sync: Enabled
Pass-through authentication: Enabled
You need to identify which users will be able to authenticate by using Microsoft Entra ID if connectivity between on-premises Active Directory and the internet is lost.
Which users should you identify?