

SC-100 Exam Question 31
You open Microsoft Defender for Cloud as shown in the following exhibit.
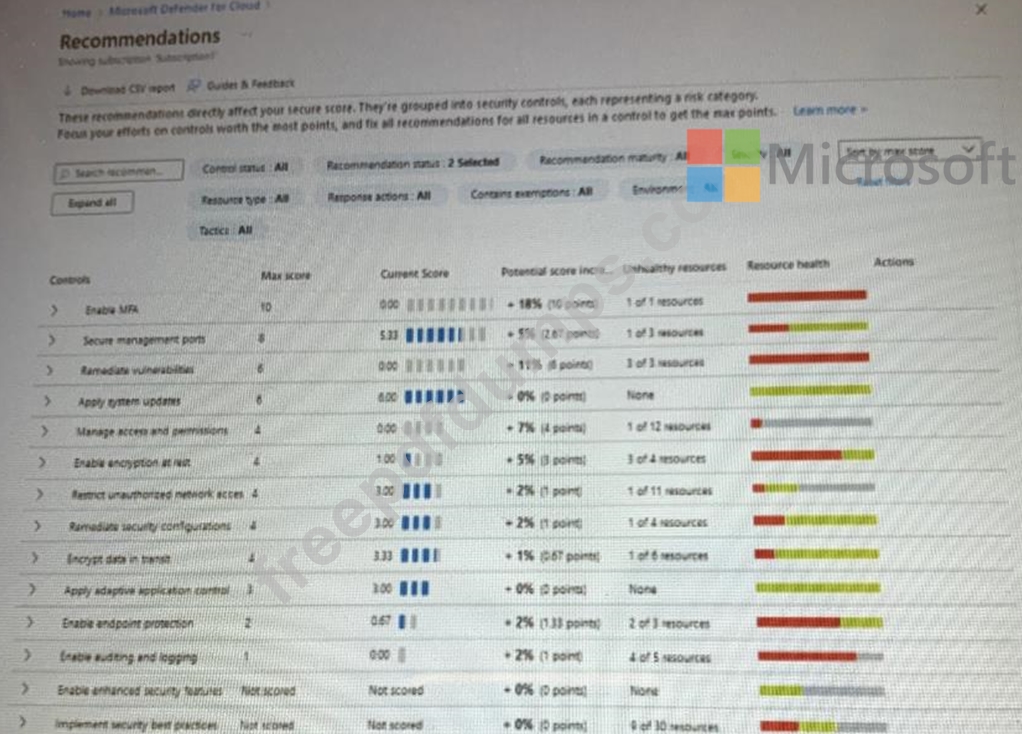
Use the drop-down menus to select the answer choice that complete each statements based on the information presented in the graphic.
NOTE: Each correct selection is worth one point.
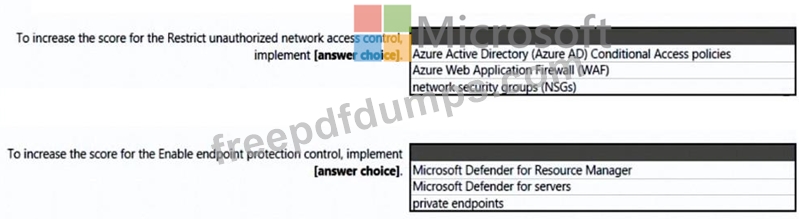
Use the drop-down menus to select the answer choice that complete each statements based on the information presented in the graphic.
NOTE: Each correct selection is worth one point.

SC-100 Exam Question 32
Your company plans to move all on-premises virtual machines to Azure. A network engineer proposes the Azure virtual network design shown in the following table.

You need to recommend an Azure Bastion deployment to provide secure remote access to all the virtual machines. Based on the virtual network design, how many Azure Bastion subnets are required?
You need to recommend an Azure Bastion deployment to provide secure remote access to all the virtual machines. Based on the virtual network design, how many Azure Bastion subnets are required?
SC-100 Exam Question 33
Your company has a Microsoft 365 E5 subscription, an Azure subscription, on-premises applications, and Active Directory Domain Services (AD DSV You need to recommend an identity security strategy that meets the following requirements:
* Ensures that customers can use their Facebook credentials to authenticate to an Azure App Service website
* Ensures that partner companies can access Microsoft SharePoint Online sites for the project to which they are assigned The solution must minimize the need to deploy additional infrastructure components. What should you include in the recommendation? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.

SC-100 Exam Question 34
Your company is moving a big data solution to Azure.
The company plans to use the following storage workloads:
* Azure Storage blob containers
* Azure Data Lake Storage Gen2
* Azure Storage file shares
* Azure Disk Storage
Which two storage workloads support authentication by using Azure Active Directory (Azure AD)?
Each correct answer presents a complete solution. NOTE: Each correct selection is worth one point.
SC-100 Exam Question 35
Your company is moving all on-premises workloads to Azure and Microsoft 365. You need to design a security orchestration, automation, and response (SOAR) strategy in Microsoft Sentinel that meets the following requirements:
* Minimizes manual intervention by security operation analysts
* Supports Waging alerts within Microsoft Teams channels
What should you include in the strategy?
* Minimizes manual intervention by security operation analysts
* Supports Waging alerts within Microsoft Teams channels
What should you include in the strategy?
Premium Bundle
Newest SC-100 Exam PDF Dumps shared by Actual4test.com for Helping Passing SC-100 Exam! Actual4test.com now offer the updated SC-100 exam dumps, the Actual4test.com SC-100 exam questions have been updated and answers have been corrected get the latest Actual4test.com SC-100 pdf dumps with Exam Engine here:
(343 Q&As Dumps, 30%OFF Special Discount: Freepdfdumps)