SC-200 Exam Question 91
You have a Microsoft Sentinel workspace named sws1.
You plan to create an Azure logic app that will raise an incident in an on-premises IT service management system when an incident is generated in sws1.
You need to configure the Microsoft Sentinel connector credentials for the logic app. The solution must meet the following requirements:
* Minimize administrative effort.
* Use the principle of least privilege.
How should you configure the credentials? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.


SC-200 Exam Question 92
You have a Microsoft subscription that has Microsoft Defender for Cloud enabled You configure the Azure logic apps shown in the following table.

You need to configure an automatic action that will run if a Suspicious process executed alert is triggered. The solution must minimize administrative effort.
Which three actions should you perform in sequence? To answer, move the appropriate actions from the list of actions to the answer area and arrange them in the correct order.

SC-200 Exam Question 93
You have an existing Azure logic app that is used to block Azure Active Directory (Azure AD) users. The logic app is triggered manually.
You deploy Azure Sentinel.
You need to use the existing logic app as a playbook in Azure Sentinel. What should you do first?
You deploy Azure Sentinel.
You need to use the existing logic app as a playbook in Azure Sentinel. What should you do first?
SC-200 Exam Question 94
You have a Microsoft 365 subscription that uses Microsoft Defender XDR.
You need to create a custom detection rule that will identify devices that had more than five antivirus detections within the last 24 hours.
how should you complete the query? To answer, select the appropriate options in the answer area.
NOTE Each correct selection is worth one point.
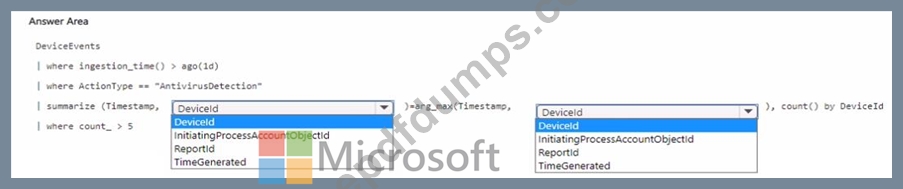
You need to create a custom detection rule that will identify devices that had more than five antivirus detections within the last 24 hours.
how should you complete the query? To answer, select the appropriate options in the answer area.
NOTE Each correct selection is worth one point.

SC-200 Exam Question 95
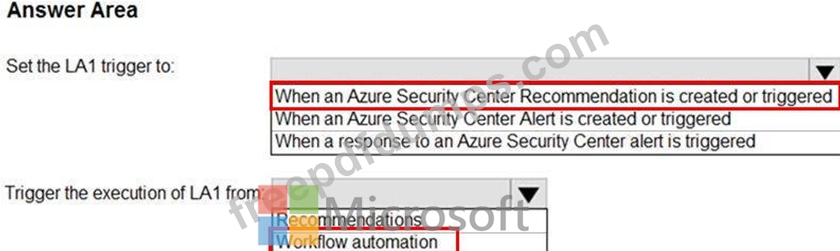
You have an Azure subscription that has Azure Defender enabled for all supported resource types.
You create an Azure logic app named LA1.
You plan to use LA1 to automatically remediate security risks detected in Azure Security Center.
You need to test LA1 in Security Center.
What should you do? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.