

CAS-004 Exam Question 156
A SOC analyst received an alert about a potential compromise and is reviewing the following SIEM logs:
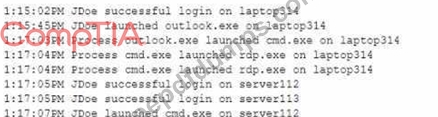
Which of the following is the most appropriate action for the SOC analyst to recommend?
Which of the following is the most appropriate action for the SOC analyst to recommend?
CAS-004 Exam Question 157
A junior developer is informed about the impact of new malware on an Advanced RISC Machine (ARM) CPU, and the code must be fixed accordingly. Based on the debug, the malware is able to insert itself in another process memory location.
Which of the following technologies can the developer enable on the ARM architecture to prevent this type of malware?
Which of the following technologies can the developer enable on the ARM architecture to prevent this type of malware?
CAS-004 Exam Question 158
A company hired a third party to develop software as part of its strategy to be quicker to market. The company's policy outlines the following requirements:
The credentials used to publish production software to the container registry should be stored in a secure location.
Access should be restricted to the pipeline service account, without the ability for the third-party developer to read the credentials directly.
Which of the following would be the BEST recommendation for storing and monitoring access to these shared credentials?
CAS-004 Exam Question 159
A security architect is implementing a web application that uses a database back end. Prior to the production, the architect is concerned about the possibility of XSS attacks and wants to identify security controls that could be put in place to prevent these attacks.
Which of the following sources could the architect consult to address this security concern?
Which of the following sources could the architect consult to address this security concern?
CAS-004 Exam Question 160
An organization requires a contractual document that includes
* An overview of what is covered
* Goals and objectives
* Performance metrics for each party
* A review of how the agreement is managed by all parties
Which of the following BEST describes this type of contractual document?
* An overview of what is covered
* Goals and objectives
* Performance metrics for each party
* A review of how the agreement is managed by all parties
Which of the following BEST describes this type of contractual document?