

CAS-004 Exam Question 181
A security architect examines a section of code and discovers the following:
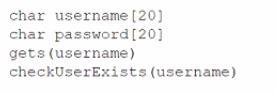
Which of the following changes should the security architect require before approving the code for release?
Which of the following changes should the security architect require before approving the code for release?
CAS-004 Exam Question 182
An analyst execute a vulnerability scan against an internet-facing DNS server and receives the following report:
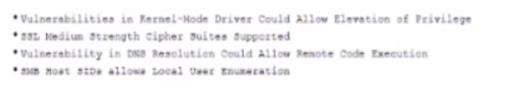
Which of the following tools should the analyst use FIRST to validate the most critical vulnerability?
Which of the following tools should the analyst use FIRST to validate the most critical vulnerability?
CAS-004 Exam Question 183
A company is moving most of its customer-facing production systems to the cloud-facing production systems to the cloud. IaaS is the service model being used. The Chief Executive Officer is concerned about the type of encryption available and requires the solution must have the highest level of security.
Which of the following encryption methods should the cloud security engineer select during the implementation phase?
Which of the following encryption methods should the cloud security engineer select during the implementation phase?
CAS-004 Exam Question 184
A local government that is investigating a data exfiltration claim was asked to review the fingerprint of the malicious user's actions. An investigator took a forensic image of the VM an downloaded the image to a secured USB drive to share with the government. Which of the following should be taken into consideration during the process of releasing the drive to the government?
CAS-004 Exam Question 185
The Chief Information Security Officer (CISO) asked a security manager to set up a system that sends an alert whenever a mobile device enters a sensitive area of the company's data center. The CISO would also like to be able to alert the individual who is entering the area that the access was logged and monitored. Which of the following would meet these requirements?