

MS-100 Exam Question 46
Your network contains an Active Directory forest named adatum.local. The forest contains 500 users and uses adatum.com as a UPN suffix.
You deploy a Microsoft 365 tenant.
You implement directory synchronization and sync only 50 support users.
You discover that five of the synchronized users have usernames that use a UPN suffix of onmicrosoft.com.
You need to ensure that all synchronized identities retain the UPN set in their on-premises user account.
What should you do?
You deploy a Microsoft 365 tenant.
You implement directory synchronization and sync only 50 support users.
You discover that five of the synchronized users have usernames that use a UPN suffix of onmicrosoft.com.
You need to ensure that all synchronized identities retain the UPN set in their on-premises user account.
What should you do?
MS-100 Exam Question 47
Which role should you assign to User1?
MS-100 Exam Question 48
You have a Microsoft 365 Enterprise E5 subscription.
You add a cloud-based app named App1 to the Microsoft Azure Active Directory (Azure AD) enterprise applications list.
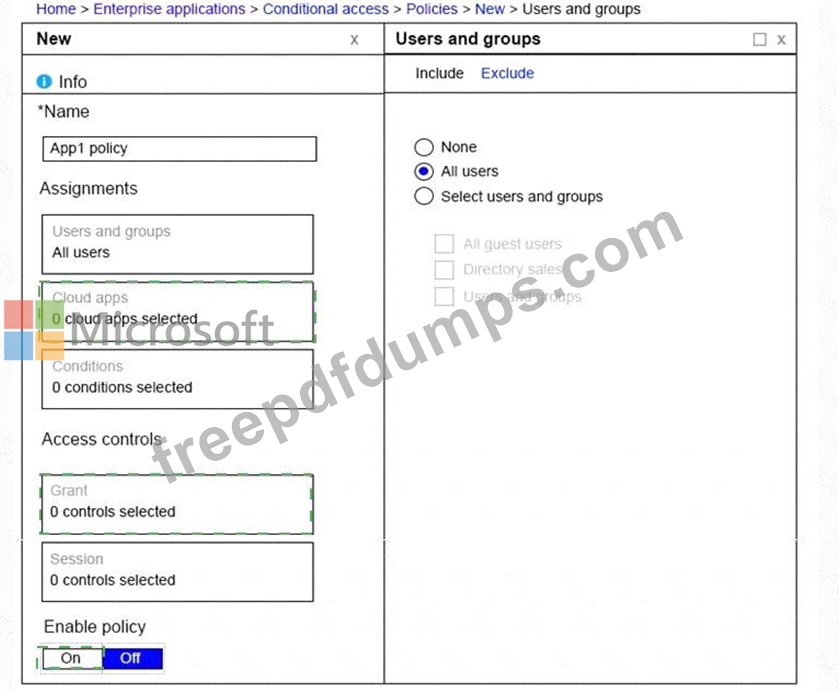
You need to ensure that two-step verification is enforced for all user accounts the next time they connect to App1.
Which three settings should you configure from the policy? To answer, select the appropriate settings in the answer area.
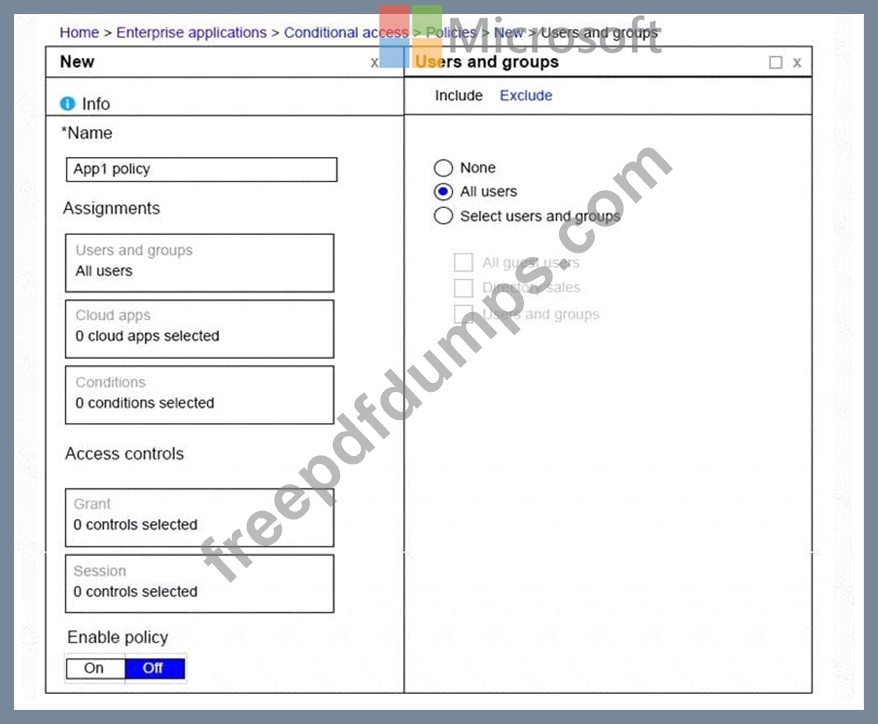
You add a cloud-based app named App1 to the Microsoft Azure Active Directory (Azure AD) enterprise applications list.
You need to ensure that two-step verification is enforced for all user accounts the next time they connect to App1.
Which three settings should you configure from the policy? To answer, select the appropriate settings in the answer area.

MS-100 Exam Question 49
Your network contains an Active Directory domain named contoso.com.
All users authenticate by using a third-party authentication solution.
You purchase Microsoft 365 and plan to implement several Microsoft 365 services.
You need to recommend an identity strategy that meets the following requirements:
* Provides seamless SSO
* Minimizes the number of additional servers required to support the solution
* Stores the passwords of all the users in Microsoft Azure Active Directory (Azure AD)
* Ensures that all the users authenticate to Microsoft 365 by using their on-premises user account You are evaluating the implementation of federation.
Which two requirements are met by using federation? Each correct answer presents a complete solution.
NOTE: Each correct selection is worth one point.
All users authenticate by using a third-party authentication solution.
You purchase Microsoft 365 and plan to implement several Microsoft 365 services.
You need to recommend an identity strategy that meets the following requirements:
* Provides seamless SSO
* Minimizes the number of additional servers required to support the solution
* Stores the passwords of all the users in Microsoft Azure Active Directory (Azure AD)
* Ensures that all the users authenticate to Microsoft 365 by using their on-premises user account You are evaluating the implementation of federation.
Which two requirements are met by using federation? Each correct answer presents a complete solution.
NOTE: Each correct selection is worth one point.
MS-100 Exam Question 50
Note: This question is part of a series of questions that present the same scenario. Each question in the series contains a unique solution that might meet the stated goals. Some question sets might have more than one correct solution, while others might not have a correct solution.
After you answer a question in this section, you will NOT be able to return to it. As a result, these questions will not appear in the review screen.
Your company plans to deploy several Microsoft Office 365 services.
You need to design an authentication strategy for the planned deployment. The solution must meet the following requirements:
* Users must be able to authenticate during business hours only.
* Authentication requests must be processed successfully if a single server fails.
* When the password for an on-premises user account expires, the new password must be enforced the next time the user signs in.
* Users who connect to Office 365 services from domain-joined devices that are connected to the internal network must be signed in automatically.
Solution: You design an authentication strategy that contains a pass-through authentication model. The solution contains two servers that have an Authentication Agent installed and password hash synchronization configured.
Does this meet the goal?
After you answer a question in this section, you will NOT be able to return to it. As a result, these questions will not appear in the review screen.
Your company plans to deploy several Microsoft Office 365 services.
You need to design an authentication strategy for the planned deployment. The solution must meet the following requirements:
* Users must be able to authenticate during business hours only.
* Authentication requests must be processed successfully if a single server fails.
* When the password for an on-premises user account expires, the new password must be enforced the next time the user signs in.
* Users who connect to Office 365 services from domain-joined devices that are connected to the internal network must be signed in automatically.
Solution: You design an authentication strategy that contains a pass-through authentication model. The solution contains two servers that have an Authentication Agent installed and password hash synchronization configured.
Does this meet the goal?