MS-102 Exam Question 61
You have a Microsoft 365 E5 tenant.
You need to create a policy that will trigger an alert when unusual Microsoft Office 365 usage patterns are detected.
What should you use to create the policy?
You need to create a policy that will trigger an alert when unusual Microsoft Office 365 usage patterns are detected.
What should you use to create the policy?
MS-102 Exam Question 62
You have a Microsoft 365 subscription.
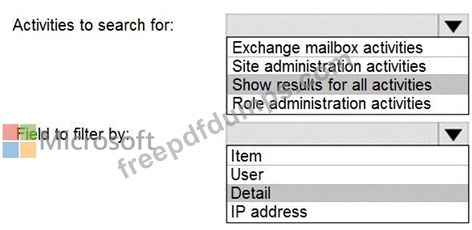
Your network uses an IP address space of 51.40.15.0/24.
An Exchange Online administrator recently created a role named Role1 from a computer on the network.
You need to identify the name of the administrator by using an audit log search.
For which activities should you search and by which field should you filter in the audit log search? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.

MS-102 Exam Question 63
You have a Microsoft 365 E5 tenant.
You create an auto-labeling policy to encrypt emails that contain a sensitive info type. You specify the locations where the policy will be applied.
You need to deploy the policy.
What should you do first?
You create an auto-labeling policy to encrypt emails that contain a sensitive info type. You specify the locations where the policy will be applied.
You need to deploy the policy.
What should you do first?
MS-102 Exam Question 64
You have a Microsoft 365 E5 subscription that contains a group named Group1. The subscription uses Microsoft Defender for Cloud Apps.
You configure cloud discovery.
You need to ensure that you can create a custom report that details shadow IT usage by the members of Group1.
What should you do first?
You configure cloud discovery.
You need to ensure that you can create a custom report that details shadow IT usage by the members of Group1.
What should you do first?
MS-102 Exam Question 65
You have a Microsoft 365 E5 subscription that includes the following active eDiscovery case:
Name: Case1
Included content: Group1, User1, Site1
Hold location: Exchange mailboxes, SharePoint sites, Exchange public folders The investigation for Case1 completes, and you close the case.
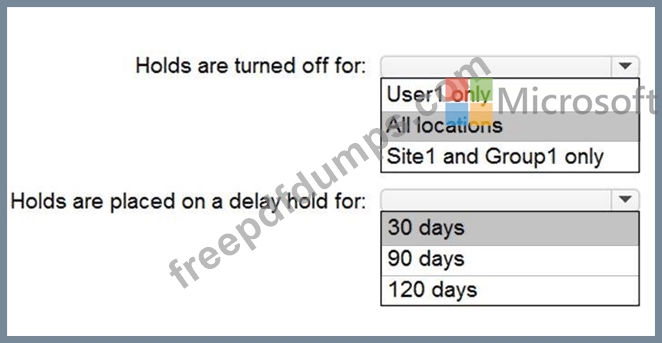
What occurs after you close Case1? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.