

SC-400 Exam Question 131
Drag and Drop Question
You have a Microsoft 365 E5 subscription that contains a user named User1.
You need to ensure that User1 can perform the following tasks:
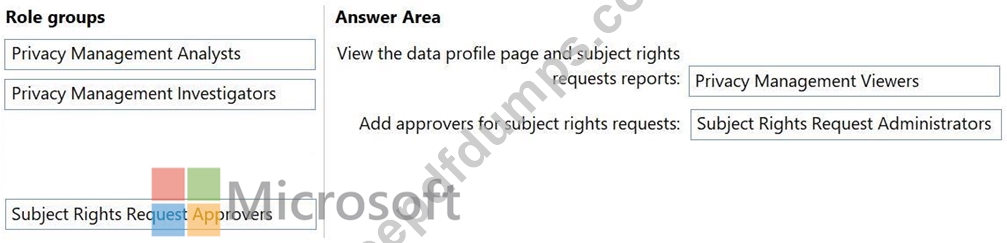
- View the Privacy risk management Data profile page and subject rights request reports.
- Add approvers for subject rights requests.
The solution must follow the principle of least privilege.
To which role group should you add User1 for each task? To answer, drag the appropriate role groups to the correct tasks. Each role group may be used once, more than once, or not at all. You may need to drag the split bar between panes or scroll to view content.
NOTE: Each correct selection is worth one point.
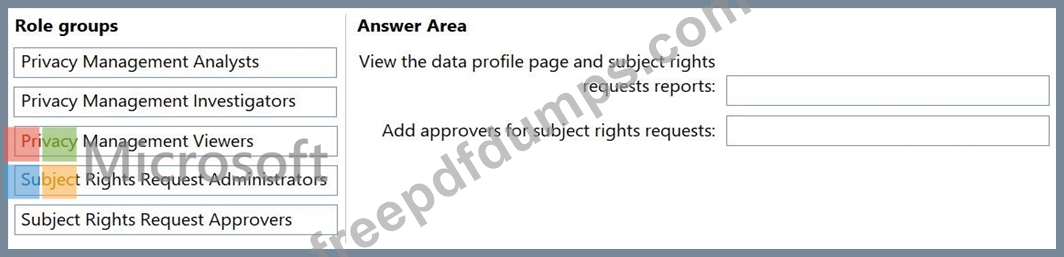
You have a Microsoft 365 E5 subscription that contains a user named User1.
You need to ensure that User1 can perform the following tasks:
- View the Privacy risk management Data profile page and subject rights request reports.
- Add approvers for subject rights requests.
The solution must follow the principle of least privilege.
To which role group should you add User1 for each task? To answer, drag the appropriate role groups to the correct tasks. Each role group may be used once, more than once, or not at all. You may need to drag the split bar between panes or scroll to view content.
NOTE: Each correct selection is worth one point.
SC-400 Exam Question 132
Case Study 2 - Contoso, Ltd
Overview
Contoso, Ltd. is a consulting company that has a main office in Montreal and three branch offices in Seattle, Boston, and Johannesburg.
Existing Environment
Microsoft 365 Environment
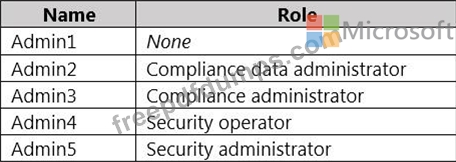
Contoso has a Microsoft 365 E5 tenant. The tenant contains the administrative user accounts shown in the following table.
Users store data in the following locations:
SharePoint sites
OneDrive accounts
Exchange email
Exchange public folders
Teams chats
Teams channel messages
When users in the research department create documents, they must add a 10-digit project code to each document. Project codes that start with the digits 999 are confidential.
SharePoint Online Environment
Contoso has four Microsoft SharePoint Online sites named Site1, Site2, Site3, and Site4.
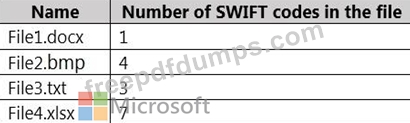
Site2 contains the files shown in the following table.
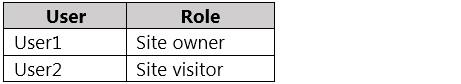
Two users named User1 and User2 are assigned roles for Site2 as shown in the following table.
Site3 stores documents related to the company's projects. The documents are organized in a folder hierarchy based on the project.
Site4 has the following two retention policies applied:
Name: Site4RetentionPolicy1
- Locations to apply the policy: Site4
- Delete items older than: 2 years
- Delete content based on: When items were created
Name: Site4RetentionPolicy2
- Locations to apply the policy: Site4
- Retain items for a specific period: 4 years
- Start the retention period based on: When items were created
- At the end of the retention period: Do nothing
Problem Statements
Management at Contoso is concerned about data leaks. On several occasions, confidential research department documents were leaked.
Requirements
Planned Changes
Contoso plans to create the following data loss prevention (DLP) policy:
Name: DLPpolicy1
Locations to apply the policy: Site2
Conditions:
- Content contains any of these sensitive info types: SWIFT Code
- Instance count: 2 to any
Actions: Restrict access to the content
Technical Requirements
Contoso must meet the following technical requirements:
All administrative users must be able to review DLP reports.
Whenever possible, the principle of least privilege must be used.
For all users, all Microsoft 365 data must be retained for at least one year.
Confidential documents must be detected and protected by using Microsoft 365.
Site1 documents that include credit card numbers must be labeled automatically.
All administrative users must be able to create Microsoft 365 sensitivity labels.
After a project is complete, the documents in Site3 that relate to the project must be retained for
10 years.
Hotspot Question
You are reviewing policies for the SharePoint Online environment.
For each of the following statements, select Yes if the statement is true. Otherwise, select No.
NOTE: Each correct selection is worth one point.

Overview
Contoso, Ltd. is a consulting company that has a main office in Montreal and three branch offices in Seattle, Boston, and Johannesburg.
Existing Environment
Microsoft 365 Environment
Contoso has a Microsoft 365 E5 tenant. The tenant contains the administrative user accounts shown in the following table.
Users store data in the following locations:
SharePoint sites
OneDrive accounts
Exchange email
Exchange public folders
Teams chats
Teams channel messages
When users in the research department create documents, they must add a 10-digit project code to each document. Project codes that start with the digits 999 are confidential.
SharePoint Online Environment
Contoso has four Microsoft SharePoint Online sites named Site1, Site2, Site3, and Site4.
Site2 contains the files shown in the following table.
Two users named User1 and User2 are assigned roles for Site2 as shown in the following table.
Site3 stores documents related to the company's projects. The documents are organized in a folder hierarchy based on the project.
Site4 has the following two retention policies applied:
Name: Site4RetentionPolicy1
- Locations to apply the policy: Site4
- Delete items older than: 2 years
- Delete content based on: When items were created
Name: Site4RetentionPolicy2
- Locations to apply the policy: Site4
- Retain items for a specific period: 4 years
- Start the retention period based on: When items were created
- At the end of the retention period: Do nothing
Problem Statements
Management at Contoso is concerned about data leaks. On several occasions, confidential research department documents were leaked.
Requirements
Planned Changes
Contoso plans to create the following data loss prevention (DLP) policy:
Name: DLPpolicy1
Locations to apply the policy: Site2
Conditions:
- Content contains any of these sensitive info types: SWIFT Code
- Instance count: 2 to any
Actions: Restrict access to the content
Technical Requirements
Contoso must meet the following technical requirements:
All administrative users must be able to review DLP reports.
Whenever possible, the principle of least privilege must be used.
For all users, all Microsoft 365 data must be retained for at least one year.
Confidential documents must be detected and protected by using Microsoft 365.
Site1 documents that include credit card numbers must be labeled automatically.
All administrative users must be able to create Microsoft 365 sensitivity labels.
After a project is complete, the documents in Site3 that relate to the project must be retained for
10 years.
Hotspot Question
You are reviewing policies for the SharePoint Online environment.
For each of the following statements, select Yes if the statement is true. Otherwise, select No.
NOTE: Each correct selection is worth one point.

SC-400 Exam Question 133
You have a Microsoft 365 E3 subscription.
You plan to assess compliance with ISO/IEC 27001:2013.
From Compliance Manager, you discover that the ISO/IEC 27001:2013 regulatory template for Microsoft 365 is inactive.
What should you do?
You plan to assess compliance with ISO/IEC 27001:2013.
From Compliance Manager, you discover that the ISO/IEC 27001:2013 regulatory template for Microsoft 365 is inactive.
What should you do?
SC-400 Exam Question 134
Note: This question is part of a series of questions that present the same scenario. Each question in the series contains a unique solution that might meet the stated goals. Some question sets might have more than one correct solution, while others might not have a correct solution.
After you answer a question in this section, you will NOT be able to return to it. As a result, these questions will not appear in the review screen.
You implement Microsoft 365 Endpoint data loss prevention (Endpoint DLP).
You have computers that run Windows 10 and have Microsoft 365 Apps installed. The computers are joined to Azure Active Directory (Azure AD).
You need to ensure that Endpoint DLP policies can protect content on the computers.
Solution: You onboard the computers to Microsoft Defender for Endpoint.
Does this meet the goal?
SC-400 Exam Question 135
You have a Microsoft 365 E5 subscription.
A security manager receives an email message every time a data loss prevention (DLP) policy match occurs.
You need to limit alert notifications to actionable DLP events.
What should you do?
A security manager receives an email message every time a data loss prevention (DLP) policy match occurs.
You need to limit alert notifications to actionable DLP events.
What should you do?
Premium Bundle
Newest SC-400 Exam PDF Dumps shared by Actual4test.com for Helping Passing SC-400 Exam! Actual4test.com now offer the updated SC-400 exam dumps, the Actual4test.com SC-400 exam questions have been updated and answers have been corrected get the latest Actual4test.com SC-400 pdf dumps with Exam Engine here:
(335 Q&As Dumps, 30%OFF Special Discount: Freepdfdumps)