

SC-400 Exam Question 146
Hotspot Question
You have a Microsoft 365 E5 subscription.
You receive the data loss prevention (DLP) alert shown in the following exhibit.

Use the drop-down menus to select the answer choice that completes each statement based on the information presented in the graphic.
NOTE: Each correct selection is worth one point.

You have a Microsoft 365 E5 subscription.
You receive the data loss prevention (DLP) alert shown in the following exhibit.
Use the drop-down menus to select the answer choice that completes each statement based on the information presented in the graphic.
NOTE: Each correct selection is worth one point.

SC-400 Exam Question 147
Case Study 1 - Fabrikam, Inc
Overview
Fabrikam, Inc. is a consulting company that has a main office in Montreal and six branch offices in New York, Seattle, Miami, Houston, Los Angeles, and Vancouver.
Existing Environment
Cloud Environment
Fabrikam has a Microsoft 365 tenant that contains the following resources:
An Azure Active Directory (Azure AD) tenant that syncs to an on-premises Active Directory domain named corp.fabrikam.com Microsoft Cloud App Security connectors configured for all supported cloud applications used by the company Some users have company Dropbox accounts.
Compliance Configuration
Fabrikam has the following in the Microsoft 365 compliance center:
A data loss prevention (DLP) policy is configured. The policy displays a tooltip to users. Users can provide a business justification to override a DLP policy violation.
The Azure Information Protection unified labeling scanner is installed and configured.
A sensitivity label named Fabrikam Confidential is configured.
An existing third-party records management system is managed by the compliance department.
Human Resources (HR) Management System
The HR department has an Azure SQL database that contains employee information. Each employee has a unique 12-character alphanumeric ID. The database contains confidential employee attributes including payroll information, date of birth, and personal contact details.
On-Premises Environment
You have an on-premises file server that runs Windows Server 2019 and stores Microsoft Office documents in a shared folder named Data.
All end-user computers are joined to the corp.fabrikam.com domain and run a third-party antimalware application.
Business Processes
Sales Contracts
Users in the sales department receive draft sales contracts from customers by email. The sales contracts are written by the customers and are not in a standard format.
Employment Applications
Employment applications and resumes are received by HR department managers and stored in either mailboxes, Microsoft SharePoint Online sites, OneDrive for Business folders, or Microsoft Teams channels.
The employment application form is downloaded from SharePoint Online and a serial number is assigned to each application.
The resumes are written by the applicants and are in any format.
Requirements
HR Requirements
You need to create a DLP policy that will notify the HR department of a DLP policy violation if a document that contains confidential employee attributes is shared externally. The DLP policy must use an Exact Data Match (EDM) classification derived from a CSV export of the HR department database.
The HR department identifies the following requirements for handling employment applications:
Resumes must be identified automatically based on similarities to other resumes received in the past.
Employment applications and resumes must be deleted automatically two years after the applications are received.
Documents and emails that contain an application serial number must be identified automatically and marked as an employment application.
Sales Requirements
A sensitivity label named Sales Contract must be applied automatically to all draft and finalized sales contracts.
Compliance Requirements
Fabrikam identifies the following compliance requirements:
All DLP policies must be applied to computers that run Windows 10, with the least possible changes to the computers.
Users in the compliance department must view the justification provided when a user receives a tooltip notification for a DLP violation.
If a document that has the Fabrikam Confidential sensitivity label applied is uploaded to Dropbox, the file must be deleted automatically.
The Fabrikam Confidential sensitivity label must be applied to existing Microsoft Word documents in the Data shared folder that have a document footer containing the following string: Company use only.
Users must be able to manually select that email messages are sent encrypted. The encryption will use Office 365 Message Encryption (OME) v2. Any email containing an attachment that has the Fabrikam Confidential sensitivity label applied must be encrypted automatically by using OME.
Existing policies configured in the third-party records management system must be replaced by using Records management in the Microsoft 365 compliance center. The compliance department plans to export the existing policies, and then produce a CSV file that contains matching labels and policies that are compatible with records management in Microsoft 365.
The CSV file must be used to configure records management in Microsoft 365.
Executive Requirements
You must be able to restore all email received by Fabrikam executives for up to three years after an email is received, even if the email was deleted permanently.
You need to recommend a solution that meets the compliance requirements for Dropbox.
What should you recommend?
SC-400 Exam Question 148
SIMULATION
Use the following login credentials as needed:
To enter your username, place your cursor in the Sign in box and click on the username below.
To enter your password, place your cursor in the Enter password box and click on the password below.
Microsoft 365 Username: [email protected]
Microsoft 365 Password: **********
If the Microsoft 365 portal does not load successfully in the browser, press CTRL-K to reload the portal in a new browser tab.
The following information is for technical support purposes only:
Lab Instance: 12345678
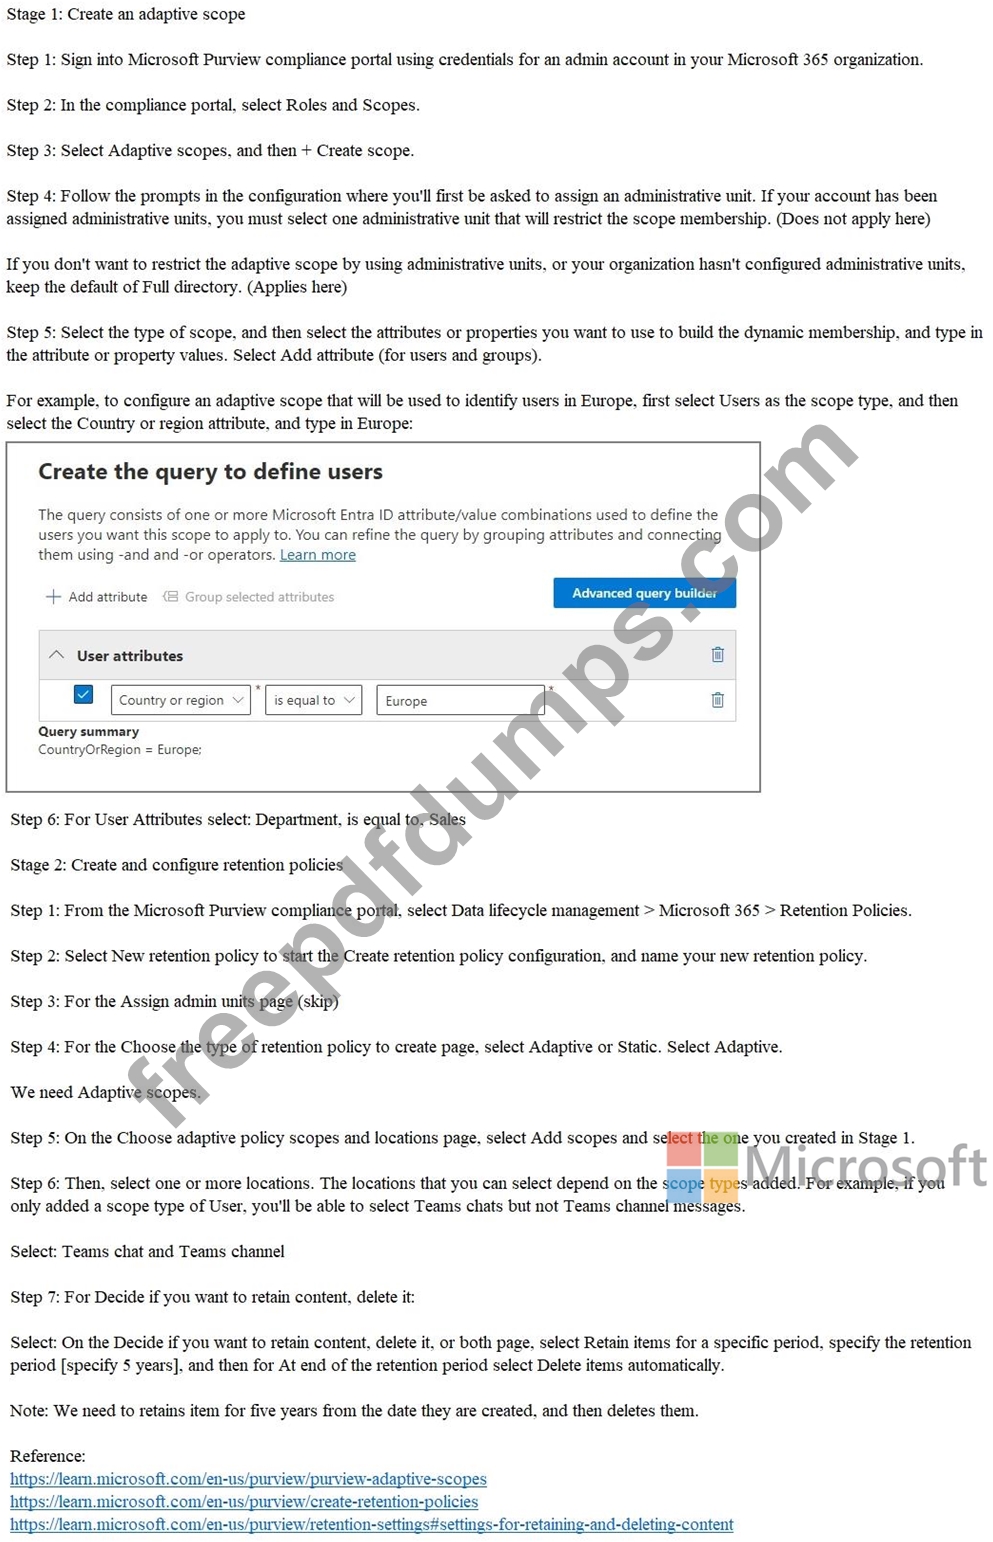
You need to create a retention policy that meets the following requirements:
- Applies to Microsoft Teams chat and Teams channel messages of users
that have a department attribute of Sales.
- Retains item for five years from the date they are created, and then
deletes them.
To complete this task, sign in to the appropriate admin center.
SC-400 Exam Question 149
Hotspot Question
You have a Microsoft 365 E5 subscription that contains the users shown in the following table.
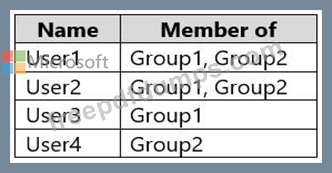
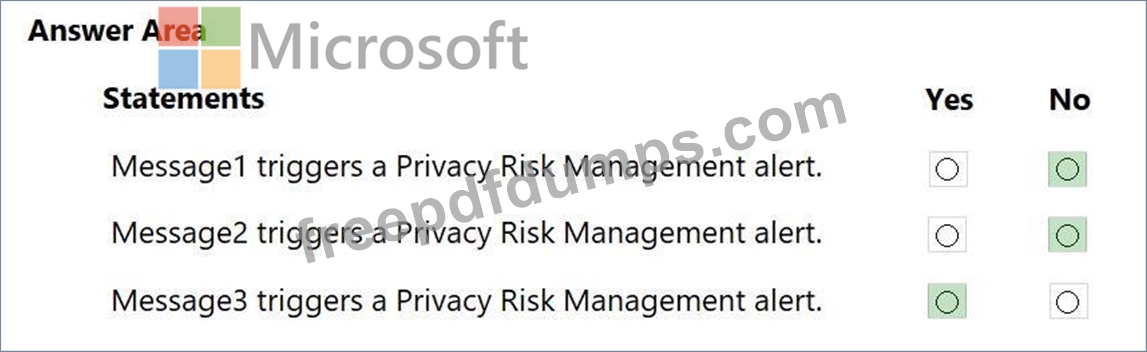
You have a Privacy Risk Management policy named Policy1 based on the Data transfers template as shown in the Privacy Risk Management policy exhibit. (Select the Privacy Risk Management policy tab and scroll to review the entire policy.)
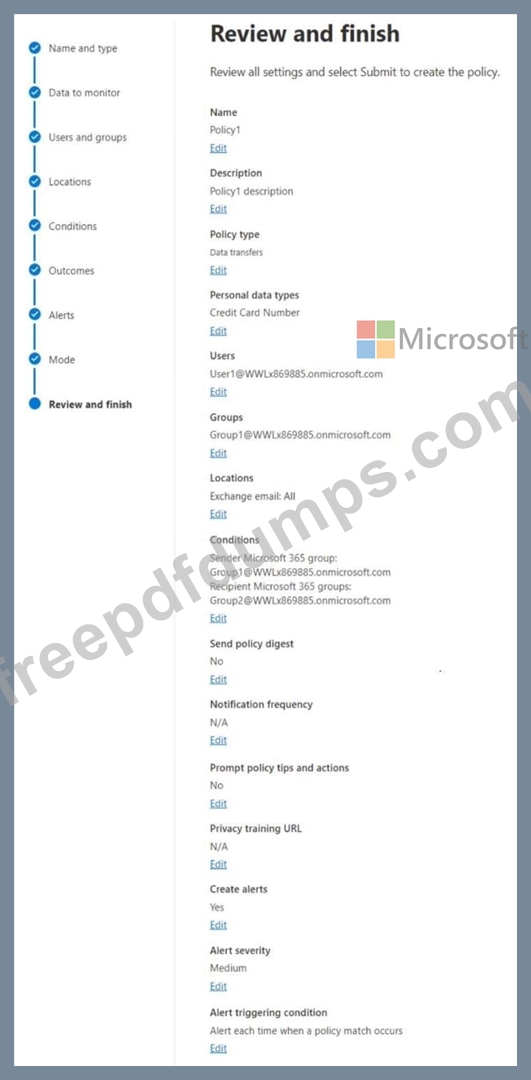
User1 sends the following email messages that contain credit card information:
- Message1: Sent to User2.
- Message2: Sent to User3.
- Message3: Sent to User4.
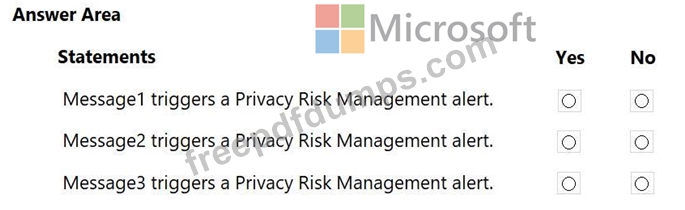
For each of the following statements, select Yes if the statement is true. Otherwise, select No.
NOTE: Each correct selection is worth one point.
You have a Microsoft 365 E5 subscription that contains the users shown in the following table.
You have a Privacy Risk Management policy named Policy1 based on the Data transfers template as shown in the Privacy Risk Management policy exhibit. (Select the Privacy Risk Management policy tab and scroll to review the entire policy.)
User1 sends the following email messages that contain credit card information:
- Message1: Sent to User2.
- Message2: Sent to User3.
- Message3: Sent to User4.
For each of the following statements, select Yes if the statement is true. Otherwise, select No.
NOTE: Each correct selection is worth one point.
SC-400 Exam Question 150
Hotspot Question
You have a Microsoft 365 E5 subscription that contains two users named User1 and User2.
You create a sensitivity label that has the following settings:
- Name: Sensitivity1
- Define the scope for this label: Items
- Choose protection settings for files and emails: Mark the content of
files
- Add custom headers, footers, and watermarks to files and emails that
have this label applied
You make Sensitivity available to User1.
User1 performs the following actions:
- Creates a new email
- Adds a file named File1.docx as an attachment to the email
- Applies Sensitivity1 to the email
- Sends the email to User2
How will the email and the attachment be marked? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
