

300-215 Exam Question 1
Which two tools conduct network traffic analysis in the absence of a graphical user interface? (Choose two.)
300-215 Exam Question 2
An engineer is analyzing a DoS attack and notices that the perpetrator used a different IP address to hide their system IP address and avoid detection. Which anti-forensics technique did the perpetrator use?
300-215 Exam Question 3
Refer to the exhibit.
Registry Key Activity
MACHINE\SOFTWARE\MICROSOFT\WINDOWS\CURRENTVERSION\RUN modified (1)
MACHINE\SOFTWARE\MICROSOFT\WINDOWS\CURRENTVERSION\RUNONCE created (1),
modified (2)
MACHINE\SOFTWARE\MICROSOFT\WINDOWS NT\CURRENTVERSION\WINLOGON modified (1) MACHINE\SYSTEM\CURRENTCONTROLSET\CONTROL\SESSION MANAGER\ENVIRONMENT modified (1) MACHINE\SOFTWARE\MICROSOFT\WINDOWS\CURRENTVERSION\POLICIES\EXPLORER modified (2) MACHINE\SOFTWARE\MICROSOFT\COMMAND PROCESSOR modified (1) For user S-5-21-0533532869, which registry key shows evidence of persistence through a newly created autorun entry?
300-215 Exam Question 4
Refer to the exhibit.
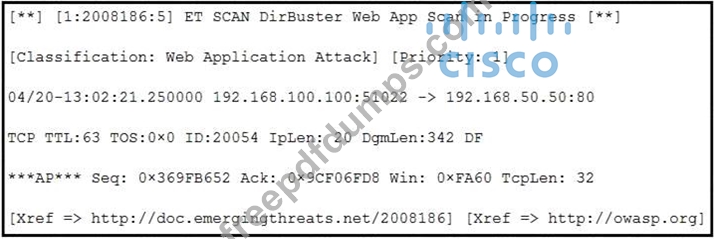
According to the SNORT alert, what is the attacker performing?
According to the SNORT alert, what is the attacker performing?
300-215 Exam Question 5
According to Cisco ISE best practices for MDM scenarios, what happens next after a user associates a device with an SSID?