

300-215 Exam Question 41
What is the purpose of YARA rules in malware analysis and now do the rules atd in identifying, classifying, and documenting malware?
300-215 Exam Question 42
A threat actor attempts to avoid detection by turning data into a code that shifts numbers to the right four times. Which anti-forensics technique is being used?
300-215 Exam Question 43
Refer to the exhibit.
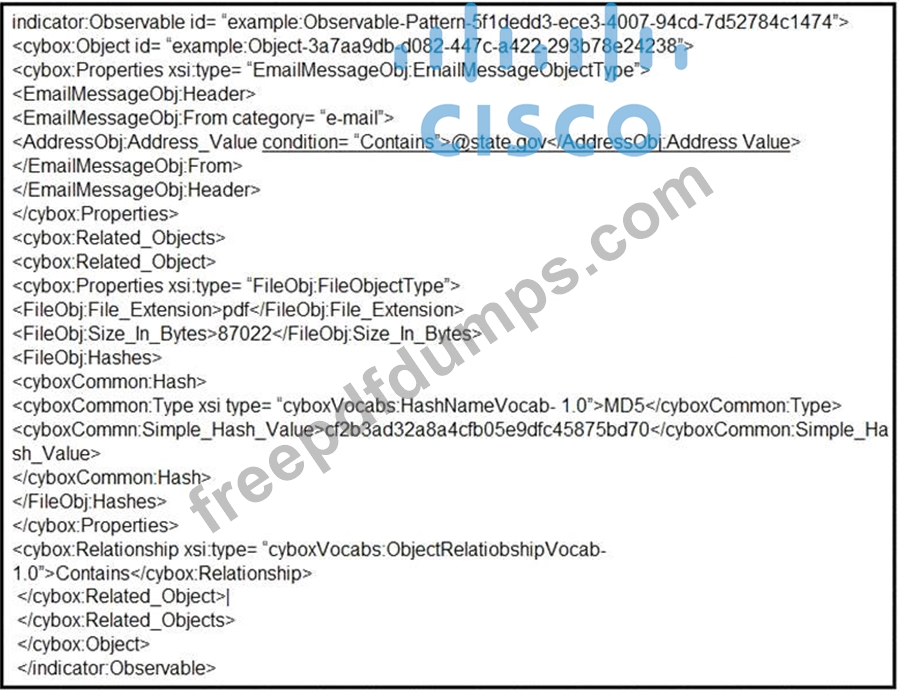
Which two actions should be taken as a result of this information? (Choose two.)
Which two actions should be taken as a result of this information? (Choose two.)
300-215 Exam Question 44
An attacker modifies a malicious file named TOPSECRET0523619132 by changing its file extension from a .
png to a doc in an attempt to evade detection. Which technique is being used to disguise the file?
png to a doc in an attempt to evade detection. Which technique is being used to disguise the file?
300-215 Exam Question 45
A company recently deployed a public web application that collects users' personal information and stores it in a database. The company is concerned that attackers could exploit application vulnerabilities to steal this information. Which approach should a security engineer recommend to identify attack vectors or attack surfaces and recommend mitigations?