300-215 Exam Question 26
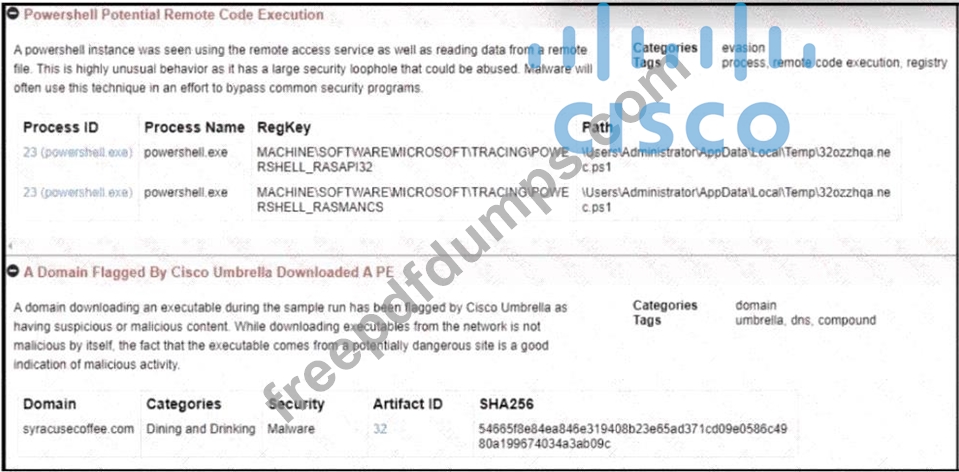
Refer to the exhibit.
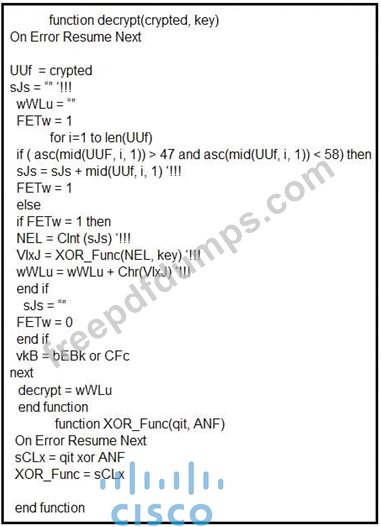
Which type of code created the snippet?
Which type of code created the snippet?
300-215 Exam Question 27
A cybersecurity analyst is investigating a high-priority incident involving a company executive's workstation.
The endpoint detection and response system flagged multiple file-modification events on the workstation. The files are normally read-only and contain sensitive financial data. The workstation's antivirus software has not detected known malware or suspicious activity, and initial dynamic analysis of the files revealed no abnormal network behavior. Given this complex scenario, what is the recommended next step?
The endpoint detection and response system flagged multiple file-modification events on the workstation. The files are normally read-only and contain sensitive financial data. The workstation's antivirus software has not detected known malware or suspicious activity, and initial dynamic analysis of the files revealed no abnormal network behavior. Given this complex scenario, what is the recommended next step?
300-215 Exam Question 28
Over the last year, an organization's HR department has accessed data from its legal department on the last day of each month to create a monthly activity report. An engineer is analyzing suspicious activity alerted by a threat intelligence platform that an authorized user in the HR department has accessed legal data daily for the last week. The engineer pulled the network data from the legal department's shared folders and discovered above average-size data dumps. Which threat actor is implied from these artifacts?
300-215 Exam Question 29
A security team received an alert of suspicious activity on a user's Internet browser. The user's anti-virus software indicated that the file attempted to create a fake recycle bin folder and connect to an external IP address. Which two actions should be taken by the security analyst with the executable file for further analysis? (Choose two.)
300-215 Exam Question 30