

CS0-004 Exam Question 1
A security analyst uses a full pcap solution to extract all traffic from the last two days associated with the
10.213.4.27 file server.
This file server is under investigation due to concerns about potential data exfiltration using Domain Name System (DNS) traffic.
Which of the following commands should the analyst use to extract any potentially leaked data from the suspicious.pcap file?
10.213.4.27 file server.
This file server is under investigation due to concerns about potential data exfiltration using Domain Name System (DNS) traffic.
Which of the following commands should the analyst use to extract any potentially leaked data from the suspicious.pcap file?
CS0-004 Exam Question 2
A vulnerability analyst must perform a security assessment on an edge device running various services.
The analyst runs an Nmap port scan and sees the following output:
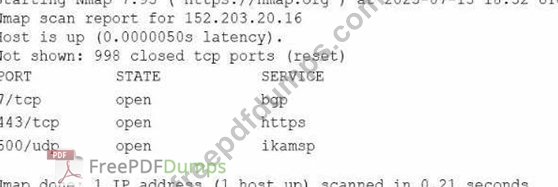
Which of the following should the analyst do next to validate the discovered remote access service is secure?
The analyst runs an Nmap port scan and sees the following output:
Which of the following should the analyst do next to validate the discovered remote access service is secure?
CS0-004 Exam Question 3
Which of the following network architectures would best implement a perimeter-less network topology?
CS0-004 Exam Question 4
An incident response team investigates a possible data leak. Various IT systems collect evidence.
Which of the following processes is required to ensure that evidentiary artifacts are properly recorded?
Which of the following processes is required to ensure that evidentiary artifacts are properly recorded?
CS0-004 Exam Question 5
A cybersecurity analyst receives an unstructured text document that contains advanced persistent threat (APT)- related indicators of compromise (IoCs). The analyst needs to extract the IPv4 addresses.
Which of the following is the best tool to accomplish this task?
Which of the following is the best tool to accomplish this task?