

CS0-004 Exam Question 16
A security analyst isolates a Windows 11 workstation from the network after known malware is detected. The list of security information and event management (SIEM) events during the malware installation and timeline does not identify a specific user who was logged in. The security analyst uses the local administrative account to log in and would like a list of logins to the machine.
Which of the following PowerShell commands should the analyst use?
Which of the following PowerShell commands should the analyst use?
CS0-004 Exam Question 17
A security analyst receives a notice about a possible data breach. The report identifies unapproved, current access dates for files found in the following personnel archives:
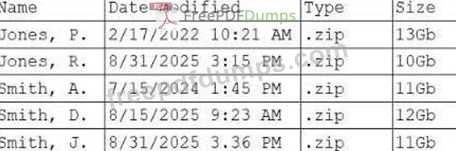
Which of the following actions should the analyst take first?
Which of the following actions should the analyst take first?
CS0-004 Exam Question 18
Which of the following best explains the purpose of the Pyramid of Pain in threat intelligence?
CS0-004 Exam Question 19
The vulnerability management team must scan the cloud environment to establish security baselines.
Which of the following assessment tools should the team use to perform this task?
Which of the following assessment tools should the team use to perform this task?
CS0-004 Exam Question 20
Which of the following is the most comprehensive type of report associated with a closed incident?