

300-215 Exam Question 51
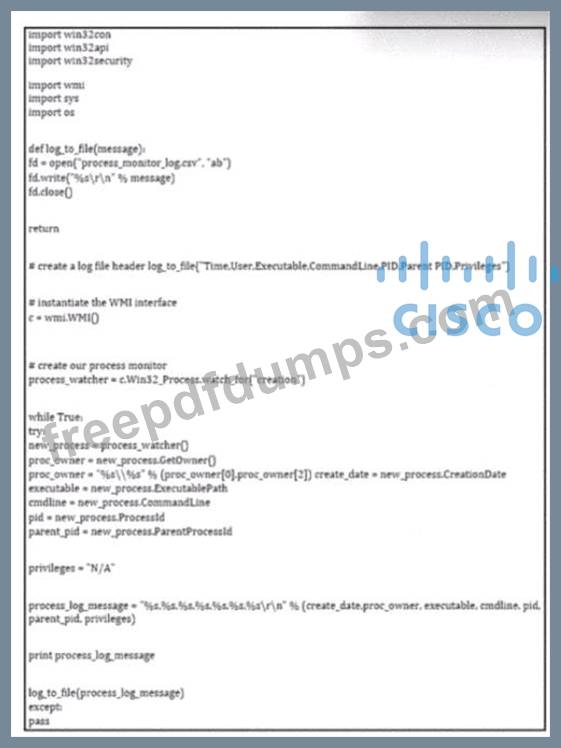
300-215 Exam Question 52
Refer to the exhibit.
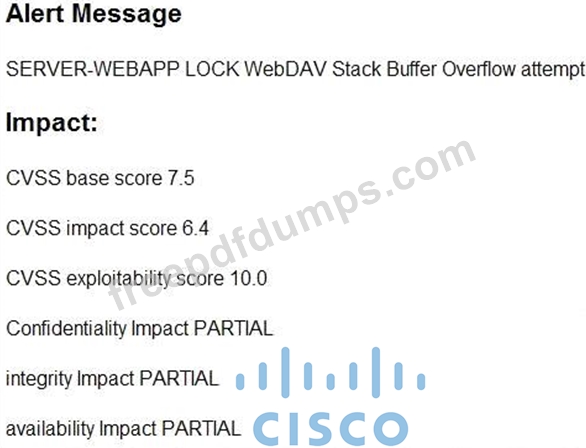
After a cyber attack, an engineer is analyzing an alert that was missed on the intrusion detection system. The attack exploited a vulnerability in a business-critical, web-based application and violated its availability.
Which two mitigation techniques should the engineer recommend? (Choose two.)
After a cyber attack, an engineer is analyzing an alert that was missed on the intrusion detection system. The attack exploited a vulnerability in a business-critical, web-based application and violated its availability.
Which two mitigation techniques should the engineer recommend? (Choose two.)
300-215 Exam Question 53
Which type of record enables forensics analysts to identify fileless malware on Windows machines?
300-215 Exam Question 54
Refer to the exhibit.

What is occurring?
What is occurring?
300-215 Exam Question 55
Refer to the exhibit.

What is the indicator of compromise?
What is the indicator of compromise?