

300-215 Exam Question 46
A company's IIS web server is breached, and the attacker accesses a Microsoft Windows Server 2016 host by exploiting an SMB vulnerability on the same subnet. The intruder shuts down critical services on the Windows server. A security engineer must retrieve the IIS logs from the web server and service-related logs from the Windows server. Which two actions accomplish this task? (Choose two.)
300-215 Exam Question 47
During a recent incident response investigation, several suspicious network connections originating from a specific host were identified. The host was quickly isolated and the machine was rebuilt During the post mortem, it became clear that there was unpreparedness regarding network artifacts necessitating adjustments to the playbooks to address this data from multiple sources must be correlated. Which two sources should be prioritized for data gathering? (Choose two.)
300-215 Exam Question 48
Refer to the exhibit.
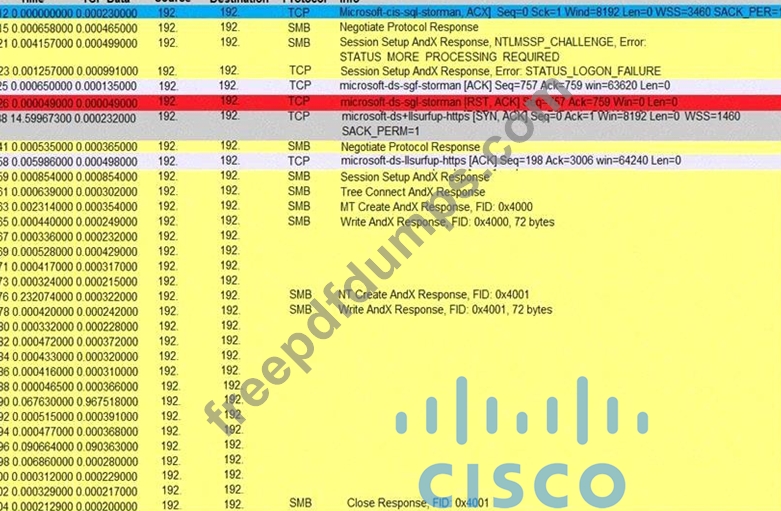
An engineer is analyzing a TCP stream in Wireshark after a suspicious email with a URL. What should be determined about the SMB traffic from this stream?
An engineer is analyzing a TCP stream in Wireshark after a suspicious email with a URL. What should be determined about the SMB traffic from this stream?
300-215 Exam Question 49
Refer to the exhibit.
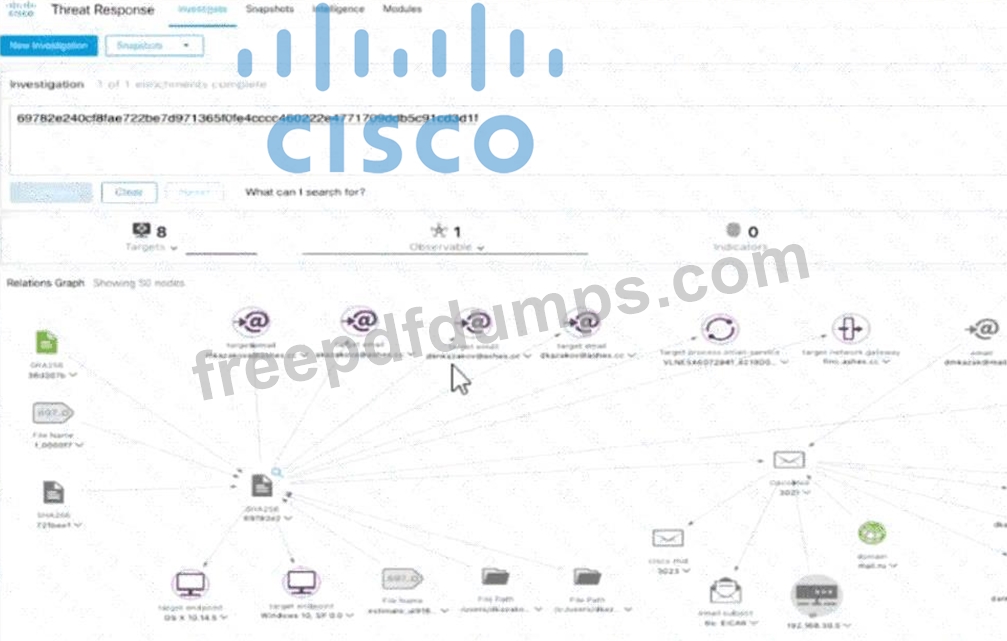
Which type of attack is occurring?
Which type of attack is occurring?
300-215 Exam Question 50
An analyst finds .xyz files of unknown origin that are large and undetected by antivirus. What action should be taken next?